Socket for Java
Secure Your Java Projects
Install our free GitHub app to protect Java dependencies from vulnerable and malicious code.
Detect and block malware, mining software, open source license violations, code quality issues, and 70+ indicators of supply chain attacks. Socket is a full-featured enterprise-ready SCA tool that can be seamlessly dropped into your workflow with just two clicks.

Socket supports Maven and Gradle
And all your favorite tools
We protect you from vulnerable and malicious Java packages
io.github.reajason:packer
2.7.1
Live on maven
Blocked by Socket
This class is an exploit/payload builder for Java deserialization vulnerabilities using Commons-Beanutils BeanComparator + PriorityQueue + TemplatesImpl gadget chain. It takes class bytes supplied via the config, embeds them in a TemplatesImpl instance, mutates private fields via reflection to craft the gadget graph, and returns a serialized representation. This is intentionally malicious (constructs remote code execution payloads) and should be treated as highly dangerous in a supply-chain context.
io.github.reajason:generator
2.7.2
Live on maven
Blocked by Socket
This class implements a WebSocket-based remote loader/webshell: it accepts binary input, optionally decrypts it with AES (using a static key), detects Java class file bytes and defines the class at runtime (using Unsafe and reflective defineClass), instantiates and executes it, and returns output/errors back over the WebSocket. This is effectively a remote code execution backdoor and should be treated as malicious and high-risk. Do not use; investigate and remove, and treat any artifact using this code as compromised.
io.github.reajason:generator
2.7.2
Live on maven
Blocked by Socket
This class is a dynamic payload loader: it decodes (base64 and optional gzip) a supplied string into class bytes, reflectively defines the class bypassing visibility, instantiates it and returns its toString(). That behavior provides an in-process arbitrary code loading and execution primitive. In a software supply-chain context this is high risk: if untrusted data can reach this method it can enable remote or local code execution, backdoors, or payload execution. Use of reflection to call defineClass with setAccessible increases the malicious potential. The code fragment itself is a loader (suspicious in libraries) and should be treated as dangerous unless its inputs are strictly controlled and validated.
org.apache.orc:orc-tools
1.9.9
Live on maven
Blocked by Socket
This DFSClient fragment contains a strong supply-chain red flag: a configuration-driven mechanism that changes NameNode RPC handling by creating a lossy proxy that proactively drops responses when enabled. That behavior can directly cause denial-of-service/availability degradation or operational sabotage if the configuration is set in production. Other components shown (address resolution, caching strategies, token/encryption wiring, checksums, hedged-read threading) appear largely typical for an HDFS client and do not, in this excerpt, indicate data theft or remote command execution.
dev.soundness:ziggurat-core
0.59.0
Live on maven
Blocked by Socket
This fragment implements a high-risk remote update/loader pattern: it fetches an artifact from an embedded URL at runtime, verifies it against an embedded SHA-256, then overwrites the executing script and re-executes it. While the hash check reduces tampering during transit, the security ultimately hinges on the integrity and trustworthiness of the embedded URL and hash within the original distributed file; if those are compromised, the script will execute attacker-controlled code. No explicit credential theft or data exfiltration is visible in this fragment, but the remote code execution/self-replacement behavior is significant in supply-chain contexts.
io.github.reajason:packer
2.9.0
Live on maven
Blocked by Socket
This script implements an unguarded dynamic JVM bytecode loader and executor. If attacker-controlled base64Str or className are possible, this is an immediate and critical remote code execution backdoor. Even if inputs are intended to be trusted, the technique is dangerous and should only be used with strong validation (cryptographic signatures, strict origin checks) and within a hardened sandbox/limited-permission ClassLoader. Treat occurrences of this code pattern as high-risk and review calling context and template injection controls before use.
org.mvnpm.at.dotenvx:primitives
1.5.1
Live on maven
Blocked by Socket
This module provides a critical arbitrary command execution capability: it executes shell commands synchronously via `execSync` for every `$(...)` embedded in parsed/evaluated values, substituting command stdout back into configuration. If an attacker can influence the parsed source text or environment variables that flow into evaluation (directly or via `runningParsed`), this becomes host RCE rather than safe templating. Additional risks include interpolation of environment-derived secrets into outputs and filesystem reads of configurable key-file paths, which amplify impact. No clear remote malware/backdoor behavior is visible in this fragment beyond the RCE primitive, but the overall security risk is extremely high unless inputs are strictly trusted.
org.eclipse.jetty.demos:jetty-servlet4-demo-jetty-webapp
12.1.12
Live on maven
Blocked by Socket
Conclusion: The servlet fragment contains severe security risks in a software supply chain context. The most critical risk is pathInfo-driven reflection that can load arbitrary classes and instantiate/throw them, enabling remote code execution or destabilizing behavior. Additional risks include input echoing in verbose HTML, input-driven delays (sleep), redirects, and broad exposure of internal state via diagnostics output. Immediate remediation should include: eliminating or strictly sanitizing the reflection path (do not load arbitrary classes from user input), validating and constraining allowed path/info inputs, removing or gating sleep-based delays, sanitizing all echoed data, removing sensitive diagnostics output, and ensuring proper access controls so that only trusted clients can trigger any potentially dangerous logic. Prefer a minimal, well-audited implementation with deterministic responses and no reflective behavior driven by untrusted inputs.
dev.anntech.flavorize:flavorize
1.1.5
Live on maven
Blocked by Socket
This module is not inherently malicious by itself, but it provides two high-risk primitives often seen in supply-chain sabotage: (1) arbitrary OS script execution via ProcessBuilder using cmd /c or bash with caller-supplied script paths and a caller-controlled working directory, and (2) SnakeYAML deserialization using Yaml.load tied to a caller-provided type. While there is no explicit network exfiltration or credential theft in the shown code, misuse or attacker influence over the inputs at call sites could enable significant compromise. Review upstream call sites for strict input/path allowlisting, confinement, and safe YAML loading configuration.
com.oracle.database.observability:ojdbc11dms
21.24.0.0
Live on maven
Blocked by Socket
High severity: this connection handler processes network notifications but also contains a magic-byte trigger (0xDE 0xAD) that sends an unexplained hardcoded 127-byte response to the connected peer, a strong indicator of hidden behavior requiring investigation. Remote packet lengths also control allocations without visible bounds checks, posing a denial-of-service risk. No external domain, URL, or fixed IP is present in the fragment; the code is not heavily obfuscated, though the triggered binary payload is embedded as byte constants.
io.github.reajason:generator
2.7.2
Live on maven
Blocked by Socket
This class is a memshell/backdoor that activates on a covert HTTP header and implements arbitrary proxying/port-forwarding and HTTP redirecting to attacker-controlled hosts. It disables TLS validation, uses reflection to hide behavior, persists streams in a static context for later reuse, and marshals data with XOR obfuscation. This is malicious by design and should be treated as a serious supply-chain/backdoor compromise: remove and investigate where it originated.
io.github.reajason:packer
2.9.0
Live on maven
Blocked by Socket
This module is a high-risk in-memory Java payload loader: it decodes an attacker-provided Base64 string into bytecode and uses sun.misc.Unsafe plus reflective JVM internal tampering to define and instantiate a new class at runtime. Because execution is triggered immediately via cc.newInstance() with no validation of the decoded bytecode, it strongly indicates malware/backdoor functionality or an exploit staging component.
io.github.reajason:generator
2.7.2
Live on maven
Blocked by Socket
This module is a highly suspicious/confirmed malicious payload loader: it uses a header/parameter trigger to Base64-decode attacker-supplied bytes into bytecode, reflectively defines that bytecode as a new JVM class (ClassLoader#defineClass with setAccessible), and instantiates it during a Struts2 request while providing HTTP request/response context. This is consistent with a Java memory shell/webshell and represents extreme security risk for any environment where it can be invoked.
io.github.reajason:generator
2.7.1
Live on maven
Blocked by Socket
This class is a clear malicious backdoor / webshell (memory-shell) for Jetty servers. It listens for a covert header/parameter combination, decrypts and loads arbitrary class bytes into the JVM (using Unsafe or defineClass via reflection), instantiates and interacts with the payload, and returns encoded output. It bypasses module and classloader protections and uses static secrets and reflection to evade detection. Do not deploy or run this component; treat as high-risk compromise and remove/scan for other implants.
io.github.reajason:generator
2.8.0
Live on maven
Blocked by Socket
This class is a backdoor webshell/memshell allowing remote actors to tunnel arbitrary TCP traffic and HTTP requests through the host application. It uses a stealth trigger header and a custom XOR-obfuscated binary protocol to receive commands and parameters, can connect to arbitrary hosts/ports (or redirect via HTTP), store persistent stream handles in memory keyed by client IDs, and deliberately disables SSL verification to permit connections to HTTPS endpoints without certificate checks. This code constitutes a malicious backdoor capable of server-side request forgery, internal network pivoting, and covert data exfiltration. It should be treated as high-risk and removed or quarantined.
com.spectralogic.ds3:ds3-metadata
5.9.0
Live on maven
Blocked by Socket
Overall, this module’s main security concern is restoreFlagsWindows: it derives an external OS command from untrusted metadata (ds3-flags) and then executes it (Runtime.exec), embedding the target path (objectName) into the command line. While the rest of the code performs plausible Windows ownership/ACL restoration using JNA and NIO APIs, the metadata-driven process execution creates a plausible supply-chain sabotage vector if attacker-controlled metadata reaches this restoration flow. Recommend strict allowlisting/escaping and removal or hardening of Runtime.exec (fixed argv array + strict grammar validation) plus logging review for sensitive path disclosure.
io.github.reajason:packer
2.9.0
Live on maven
Blocked by Socket
This class is a payload/gadget packer that assembles a Java deserialization gadget chain (Commons BeanUtils 1.9 + TemplatesImpl inside a PriorityQueue) from provided class bytes and returns a serialized payload string. The behavior is consistent with an exploit generator intended to produce objects that will execute supplied bytecode when deserialized by a vulnerable target. This is malicious in the context of systems where deserialization occurs on untrusted data and should not be used in benign applications.
com.zhuozhengsoft:pageoffice
6.7.0.1-javax
Live on maven
Blocked by Socket
This module exhibits multiple high-severity supply-chain/sandbox escape indicators: it executes eval() on network-derived data (remote code execution), supports RPC-like invocation of window functions based on externally supplied method names (remote control), and transmits sensitive browser state (document.cookie and serialized storage/headers) to backend endpoints. It also includes an arbitrary script injection primitive and permissive postMessage bridging. Treat this dependency as highly dangerous and review/contain aggressively (e.g., remove eval/dynamic invocation, block cookie/state exfiltration, enforce strict origin checks, and remove or lock down dynamic script loading).
dev.soundness:ziggurat-core
0.63.0
Live on maven
Blocked by Socket
This fragment is a classic self-unpacking Windows batch dropper/launcher: it extracts architecture-specific encoded blobs from its own script text, decodes them with `certutil -decode`, writes a runnable `.exe` beside the script, and then deletes the batch and intermediate files while executing the dropped binary. The absence of any integrity verification makes the decoded payload a high-risk element in a supply-chain context. While network/persistence/credential theft are not shown in this fragment, the payload-dropping and execution behavior alone is strongly suspicious and warrants treating the produced `%~dpn0.exe` as potentially malicious until inspected (hash/signature and runtime behavior).
org.apache.struts:struts2-showcase
7.4.0
Live on maven
Blocked by Socket
The code can modify server-side JSP resources at runtime using unvalidated external input, including dangerous overwrite and destructive truncation of critical files. This represents a severe security and supply-chain risk, potentially enabling backdoors or content tampering in deployed applications. Remediation should include strict input validation, removal of runtime filesystem writes to JSP resources, and removal of any destructive clean-up paths.
io.github.reajason:generator
2.8.0
Live on maven
Blocked by Socket
This class implements a memory-resident webshell/backdoor: it listens for specially-marked HTTP requests (controlled by headerName/headerValue), decodes and decrypts supplied bytecode, uses Unsafe/reflective defineClass to load it into the JVM, instantiates it, and returns encoded results. This enables arbitrary remote code execution inside the process and is a high-risk malicious component. Do not use; remove and investigate runtime impact and any persisted presence. Recommend incident response steps: isolate host, scan for similar classes, check static field values and where class was introduced, and rotate any credentials possibly exposed by the payload.
org.eclipse.jetty.demos:jetty-servlet4-demo-jetty-webapp
12.1.13
Live on maven
Blocked by Socket
Conclusion: The servlet fragment contains severe security risks in a software supply chain context. The most critical risk is pathInfo-driven reflection that can load arbitrary classes and instantiate/throw them, enabling remote code execution or destabilizing behavior. Additional risks include input echoing in verbose HTML, input-driven delays (sleep), redirects, and broad exposure of internal state via diagnostics output. Immediate remediation should include: eliminating or strictly sanitizing the reflection path (do not load arbitrary classes from user input), validating and constraining allowed path/info inputs, removing or gating sleep-based delays, sanitizing all echoed data, removing sensitive diagnostics output, and ensuring proper access controls so that only trusted clients can trigger any potentially dangerous logic. Prefer a minimal, well-audited implementation with deterministic responses and no reflective behavior driven by untrusted inputs.
io.github.reajason:generator
2.7.2
Live on maven
Blocked by Socket
This class is a malicious Tomcat memshell/backdoor. It listens for requests containing a specific header and content-type, unmarshals a custom binary protocol, and can open outbound TCP or HTTP(S) connections, proxy bidirectional data over HTTP, and maintain persistent in-memory channels via a ctx map. It disables SSL verification for HTTPS outbound connections (hostname verifier always returns true and TrustManager is inert). The behavior allows remote access and data exfiltration; therefore the code should be treated as high risk and removed/blocked.
dev.soundness:ziggurat-core
0.63.0
Live on maven
Blocked by Socket
This fragment implements a high-risk remote update/loader pattern: it fetches an artifact from an embedded URL at runtime, verifies it against an embedded SHA-256, then overwrites the executing script and re-executes it. While the hash check reduces tampering during transit, the security ultimately hinges on the integrity and trustworthiness of the embedded URL and hash within the original distributed file; if those are compromised, the script will execute attacker-controlled code. No explicit credential theft or data exfiltration is visible in this fragment, but the remote code execution/self-replacement behavior is significant in supply-chain contexts.
io.github.reajason:generator
2.8.0
Live on maven
Blocked by Socket
This class implements a WebSocket-based remote loader/webshell: it accepts binary input, optionally decrypts it with AES (using a static key), detects Java class file bytes and defines the class at runtime (using Unsafe and reflective defineClass), instantiates and executes it, and returns output/errors back over the WebSocket. This is effectively a remote code execution backdoor and should be treated as malicious and high-risk. Do not use; investigate and remove, and treat any artifact using this code as compromised.
io.github.reajason:packer
2.7.1
Live on maven
Blocked by Socket
This class is an exploit/payload builder for Java deserialization vulnerabilities using Commons-Beanutils BeanComparator + PriorityQueue + TemplatesImpl gadget chain. It takes class bytes supplied via the config, embeds them in a TemplatesImpl instance, mutates private fields via reflection to craft the gadget graph, and returns a serialized representation. This is intentionally malicious (constructs remote code execution payloads) and should be treated as highly dangerous in a supply-chain context.
io.github.reajason:generator
2.7.2
Live on maven
Blocked by Socket
This class implements a WebSocket-based remote loader/webshell: it accepts binary input, optionally decrypts it with AES (using a static key), detects Java class file bytes and defines the class at runtime (using Unsafe and reflective defineClass), instantiates and executes it, and returns output/errors back over the WebSocket. This is effectively a remote code execution backdoor and should be treated as malicious and high-risk. Do not use; investigate and remove, and treat any artifact using this code as compromised.
io.github.reajason:generator
2.7.2
Live on maven
Blocked by Socket
This class is a dynamic payload loader: it decodes (base64 and optional gzip) a supplied string into class bytes, reflectively defines the class bypassing visibility, instantiates it and returns its toString(). That behavior provides an in-process arbitrary code loading and execution primitive. In a software supply-chain context this is high risk: if untrusted data can reach this method it can enable remote or local code execution, backdoors, or payload execution. Use of reflection to call defineClass with setAccessible increases the malicious potential. The code fragment itself is a loader (suspicious in libraries) and should be treated as dangerous unless its inputs are strictly controlled and validated.
org.apache.orc:orc-tools
1.9.9
Live on maven
Blocked by Socket
This DFSClient fragment contains a strong supply-chain red flag: a configuration-driven mechanism that changes NameNode RPC handling by creating a lossy proxy that proactively drops responses when enabled. That behavior can directly cause denial-of-service/availability degradation or operational sabotage if the configuration is set in production. Other components shown (address resolution, caching strategies, token/encryption wiring, checksums, hedged-read threading) appear largely typical for an HDFS client and do not, in this excerpt, indicate data theft or remote command execution.
dev.soundness:ziggurat-core
0.59.0
Live on maven
Blocked by Socket
This fragment implements a high-risk remote update/loader pattern: it fetches an artifact from an embedded URL at runtime, verifies it against an embedded SHA-256, then overwrites the executing script and re-executes it. While the hash check reduces tampering during transit, the security ultimately hinges on the integrity and trustworthiness of the embedded URL and hash within the original distributed file; if those are compromised, the script will execute attacker-controlled code. No explicit credential theft or data exfiltration is visible in this fragment, but the remote code execution/self-replacement behavior is significant in supply-chain contexts.
io.github.reajason:packer
2.9.0
Live on maven
Blocked by Socket
This script implements an unguarded dynamic JVM bytecode loader and executor. If attacker-controlled base64Str or className are possible, this is an immediate and critical remote code execution backdoor. Even if inputs are intended to be trusted, the technique is dangerous and should only be used with strong validation (cryptographic signatures, strict origin checks) and within a hardened sandbox/limited-permission ClassLoader. Treat occurrences of this code pattern as high-risk and review calling context and template injection controls before use.
org.mvnpm.at.dotenvx:primitives
1.5.1
Live on maven
Blocked by Socket
This module provides a critical arbitrary command execution capability: it executes shell commands synchronously via `execSync` for every `$(...)` embedded in parsed/evaluated values, substituting command stdout back into configuration. If an attacker can influence the parsed source text or environment variables that flow into evaluation (directly or via `runningParsed`), this becomes host RCE rather than safe templating. Additional risks include interpolation of environment-derived secrets into outputs and filesystem reads of configurable key-file paths, which amplify impact. No clear remote malware/backdoor behavior is visible in this fragment beyond the RCE primitive, but the overall security risk is extremely high unless inputs are strictly trusted.
org.eclipse.jetty.demos:jetty-servlet4-demo-jetty-webapp
12.1.12
Live on maven
Blocked by Socket
Conclusion: The servlet fragment contains severe security risks in a software supply chain context. The most critical risk is pathInfo-driven reflection that can load arbitrary classes and instantiate/throw them, enabling remote code execution or destabilizing behavior. Additional risks include input echoing in verbose HTML, input-driven delays (sleep), redirects, and broad exposure of internal state via diagnostics output. Immediate remediation should include: eliminating or strictly sanitizing the reflection path (do not load arbitrary classes from user input), validating and constraining allowed path/info inputs, removing or gating sleep-based delays, sanitizing all echoed data, removing sensitive diagnostics output, and ensuring proper access controls so that only trusted clients can trigger any potentially dangerous logic. Prefer a minimal, well-audited implementation with deterministic responses and no reflective behavior driven by untrusted inputs.
dev.anntech.flavorize:flavorize
1.1.5
Live on maven
Blocked by Socket
This module is not inherently malicious by itself, but it provides two high-risk primitives often seen in supply-chain sabotage: (1) arbitrary OS script execution via ProcessBuilder using cmd /c or bash with caller-supplied script paths and a caller-controlled working directory, and (2) SnakeYAML deserialization using Yaml.load tied to a caller-provided type. While there is no explicit network exfiltration or credential theft in the shown code, misuse or attacker influence over the inputs at call sites could enable significant compromise. Review upstream call sites for strict input/path allowlisting, confinement, and safe YAML loading configuration.
com.oracle.database.observability:ojdbc11dms
21.24.0.0
Live on maven
Blocked by Socket
High severity: this connection handler processes network notifications but also contains a magic-byte trigger (0xDE 0xAD) that sends an unexplained hardcoded 127-byte response to the connected peer, a strong indicator of hidden behavior requiring investigation. Remote packet lengths also control allocations without visible bounds checks, posing a denial-of-service risk. No external domain, URL, or fixed IP is present in the fragment; the code is not heavily obfuscated, though the triggered binary payload is embedded as byte constants.
io.github.reajason:generator
2.7.2
Live on maven
Blocked by Socket
This class is a memshell/backdoor that activates on a covert HTTP header and implements arbitrary proxying/port-forwarding and HTTP redirecting to attacker-controlled hosts. It disables TLS validation, uses reflection to hide behavior, persists streams in a static context for later reuse, and marshals data with XOR obfuscation. This is malicious by design and should be treated as a serious supply-chain/backdoor compromise: remove and investigate where it originated.
io.github.reajason:packer
2.9.0
Live on maven
Blocked by Socket
This module is a high-risk in-memory Java payload loader: it decodes an attacker-provided Base64 string into bytecode and uses sun.misc.Unsafe plus reflective JVM internal tampering to define and instantiate a new class at runtime. Because execution is triggered immediately via cc.newInstance() with no validation of the decoded bytecode, it strongly indicates malware/backdoor functionality or an exploit staging component.
io.github.reajason:generator
2.7.2
Live on maven
Blocked by Socket
This module is a highly suspicious/confirmed malicious payload loader: it uses a header/parameter trigger to Base64-decode attacker-supplied bytes into bytecode, reflectively defines that bytecode as a new JVM class (ClassLoader#defineClass with setAccessible), and instantiates it during a Struts2 request while providing HTTP request/response context. This is consistent with a Java memory shell/webshell and represents extreme security risk for any environment where it can be invoked.
io.github.reajason:generator
2.7.1
Live on maven
Blocked by Socket
This class is a clear malicious backdoor / webshell (memory-shell) for Jetty servers. It listens for a covert header/parameter combination, decrypts and loads arbitrary class bytes into the JVM (using Unsafe or defineClass via reflection), instantiates and interacts with the payload, and returns encoded output. It bypasses module and classloader protections and uses static secrets and reflection to evade detection. Do not deploy or run this component; treat as high-risk compromise and remove/scan for other implants.
io.github.reajason:generator
2.8.0
Live on maven
Blocked by Socket
This class is a backdoor webshell/memshell allowing remote actors to tunnel arbitrary TCP traffic and HTTP requests through the host application. It uses a stealth trigger header and a custom XOR-obfuscated binary protocol to receive commands and parameters, can connect to arbitrary hosts/ports (or redirect via HTTP), store persistent stream handles in memory keyed by client IDs, and deliberately disables SSL verification to permit connections to HTTPS endpoints without certificate checks. This code constitutes a malicious backdoor capable of server-side request forgery, internal network pivoting, and covert data exfiltration. It should be treated as high-risk and removed or quarantined.
com.spectralogic.ds3:ds3-metadata
5.9.0
Live on maven
Blocked by Socket
Overall, this module’s main security concern is restoreFlagsWindows: it derives an external OS command from untrusted metadata (ds3-flags) and then executes it (Runtime.exec), embedding the target path (objectName) into the command line. While the rest of the code performs plausible Windows ownership/ACL restoration using JNA and NIO APIs, the metadata-driven process execution creates a plausible supply-chain sabotage vector if attacker-controlled metadata reaches this restoration flow. Recommend strict allowlisting/escaping and removal or hardening of Runtime.exec (fixed argv array + strict grammar validation) plus logging review for sensitive path disclosure.
io.github.reajason:packer
2.9.0
Live on maven
Blocked by Socket
This class is a payload/gadget packer that assembles a Java deserialization gadget chain (Commons BeanUtils 1.9 + TemplatesImpl inside a PriorityQueue) from provided class bytes and returns a serialized payload string. The behavior is consistent with an exploit generator intended to produce objects that will execute supplied bytecode when deserialized by a vulnerable target. This is malicious in the context of systems where deserialization occurs on untrusted data and should not be used in benign applications.
com.zhuozhengsoft:pageoffice
6.7.0.1-javax
Live on maven
Blocked by Socket
This module exhibits multiple high-severity supply-chain/sandbox escape indicators: it executes eval() on network-derived data (remote code execution), supports RPC-like invocation of window functions based on externally supplied method names (remote control), and transmits sensitive browser state (document.cookie and serialized storage/headers) to backend endpoints. It also includes an arbitrary script injection primitive and permissive postMessage bridging. Treat this dependency as highly dangerous and review/contain aggressively (e.g., remove eval/dynamic invocation, block cookie/state exfiltration, enforce strict origin checks, and remove or lock down dynamic script loading).
dev.soundness:ziggurat-core
0.63.0
Live on maven
Blocked by Socket
This fragment is a classic self-unpacking Windows batch dropper/launcher: it extracts architecture-specific encoded blobs from its own script text, decodes them with `certutil -decode`, writes a runnable `.exe` beside the script, and then deletes the batch and intermediate files while executing the dropped binary. The absence of any integrity verification makes the decoded payload a high-risk element in a supply-chain context. While network/persistence/credential theft are not shown in this fragment, the payload-dropping and execution behavior alone is strongly suspicious and warrants treating the produced `%~dpn0.exe` as potentially malicious until inspected (hash/signature and runtime behavior).
org.apache.struts:struts2-showcase
7.4.0
Live on maven
Blocked by Socket
The code can modify server-side JSP resources at runtime using unvalidated external input, including dangerous overwrite and destructive truncation of critical files. This represents a severe security and supply-chain risk, potentially enabling backdoors or content tampering in deployed applications. Remediation should include strict input validation, removal of runtime filesystem writes to JSP resources, and removal of any destructive clean-up paths.
io.github.reajason:generator
2.8.0
Live on maven
Blocked by Socket
This class implements a memory-resident webshell/backdoor: it listens for specially-marked HTTP requests (controlled by headerName/headerValue), decodes and decrypts supplied bytecode, uses Unsafe/reflective defineClass to load it into the JVM, instantiates it, and returns encoded results. This enables arbitrary remote code execution inside the process and is a high-risk malicious component. Do not use; remove and investigate runtime impact and any persisted presence. Recommend incident response steps: isolate host, scan for similar classes, check static field values and where class was introduced, and rotate any credentials possibly exposed by the payload.
org.eclipse.jetty.demos:jetty-servlet4-demo-jetty-webapp
12.1.13
Live on maven
Blocked by Socket
Conclusion: The servlet fragment contains severe security risks in a software supply chain context. The most critical risk is pathInfo-driven reflection that can load arbitrary classes and instantiate/throw them, enabling remote code execution or destabilizing behavior. Additional risks include input echoing in verbose HTML, input-driven delays (sleep), redirects, and broad exposure of internal state via diagnostics output. Immediate remediation should include: eliminating or strictly sanitizing the reflection path (do not load arbitrary classes from user input), validating and constraining allowed path/info inputs, removing or gating sleep-based delays, sanitizing all echoed data, removing sensitive diagnostics output, and ensuring proper access controls so that only trusted clients can trigger any potentially dangerous logic. Prefer a minimal, well-audited implementation with deterministic responses and no reflective behavior driven by untrusted inputs.
io.github.reajason:generator
2.7.2
Live on maven
Blocked by Socket
This class is a malicious Tomcat memshell/backdoor. It listens for requests containing a specific header and content-type, unmarshals a custom binary protocol, and can open outbound TCP or HTTP(S) connections, proxy bidirectional data over HTTP, and maintain persistent in-memory channels via a ctx map. It disables SSL verification for HTTPS outbound connections (hostname verifier always returns true and TrustManager is inert). The behavior allows remote access and data exfiltration; therefore the code should be treated as high risk and removed/blocked.
dev.soundness:ziggurat-core
0.63.0
Live on maven
Blocked by Socket
This fragment implements a high-risk remote update/loader pattern: it fetches an artifact from an embedded URL at runtime, verifies it against an embedded SHA-256, then overwrites the executing script and re-executes it. While the hash check reduces tampering during transit, the security ultimately hinges on the integrity and trustworthiness of the embedded URL and hash within the original distributed file; if those are compromised, the script will execute attacker-controlled code. No explicit credential theft or data exfiltration is visible in this fragment, but the remote code execution/self-replacement behavior is significant in supply-chain contexts.
io.github.reajason:generator
2.8.0
Live on maven
Blocked by Socket
This class implements a WebSocket-based remote loader/webshell: it accepts binary input, optionally decrypts it with AES (using a static key), detects Java class file bytes and defines the class at runtime (using Unsafe and reflective defineClass), instantiates and executes it, and returns output/errors back over the WebSocket. This is effectively a remote code execution backdoor and should be treated as malicious and high-risk. Do not use; investigate and remove, and treat any artifact using this code as compromised.
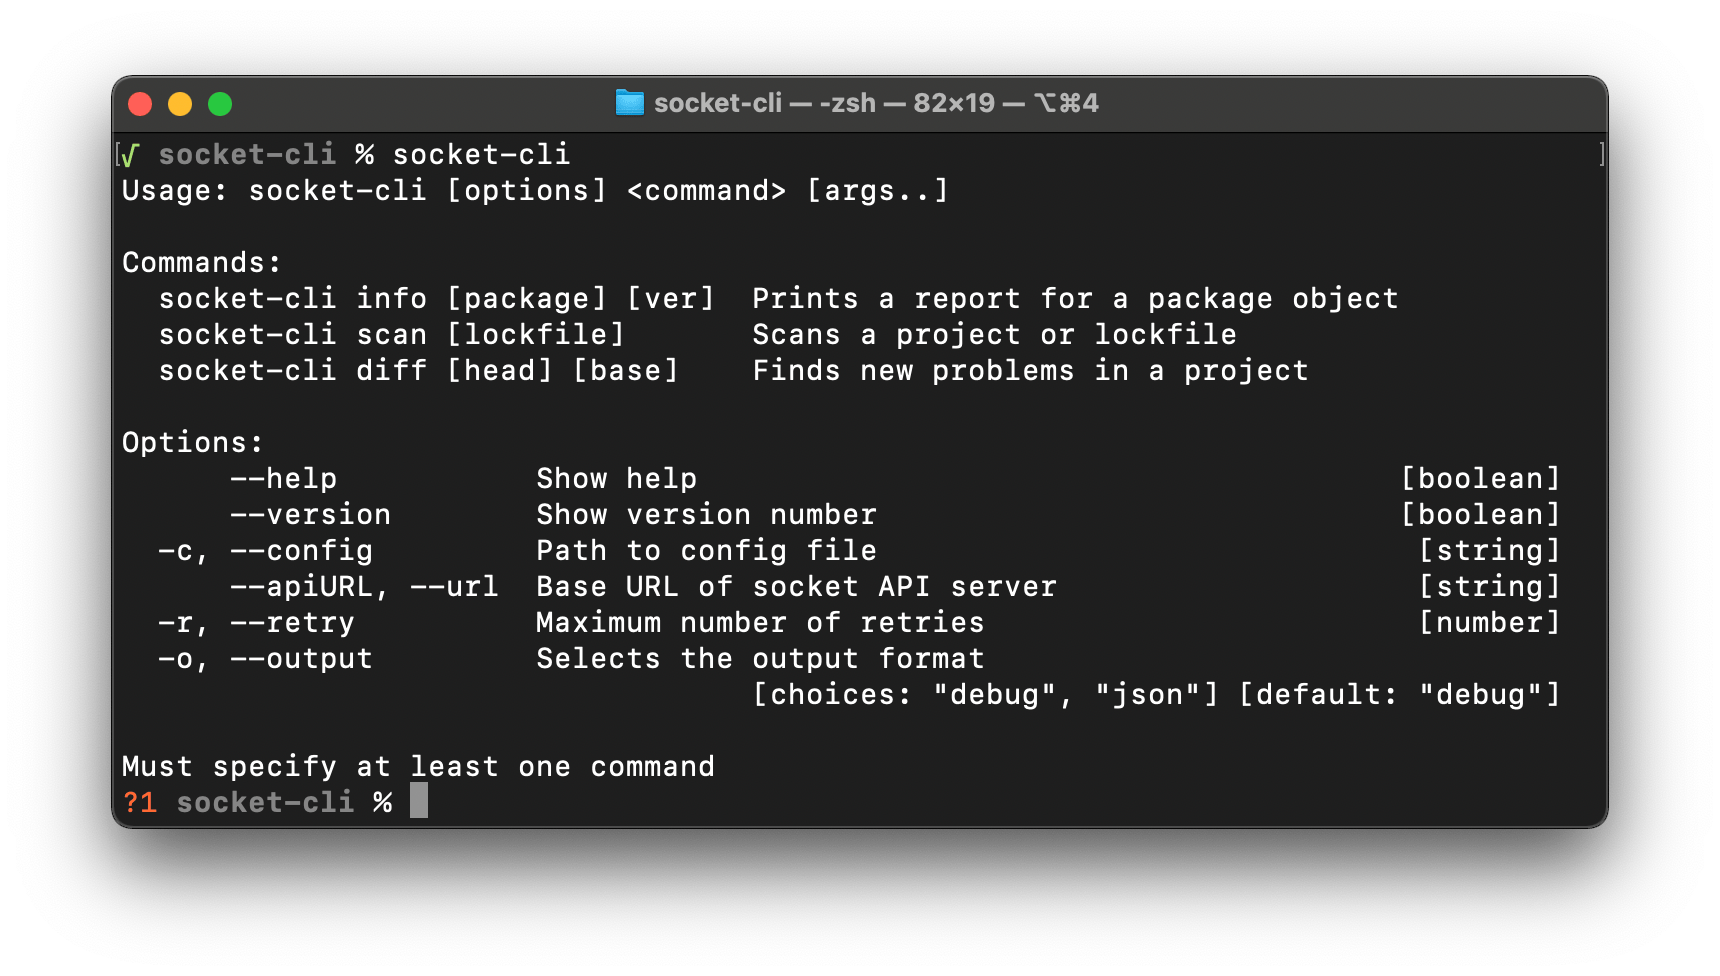
Socket CLI
Not using GitHub? Generate reports next to your tests with our CLI
We help security teams work more efficiently
Cut through the noise and focus on real threats.
Get actionable alerts for the supply chain risks that matter. Socket highlights risky dependencies directly within the developer workflow.