Impressum-Check DE: Pflichtangaben
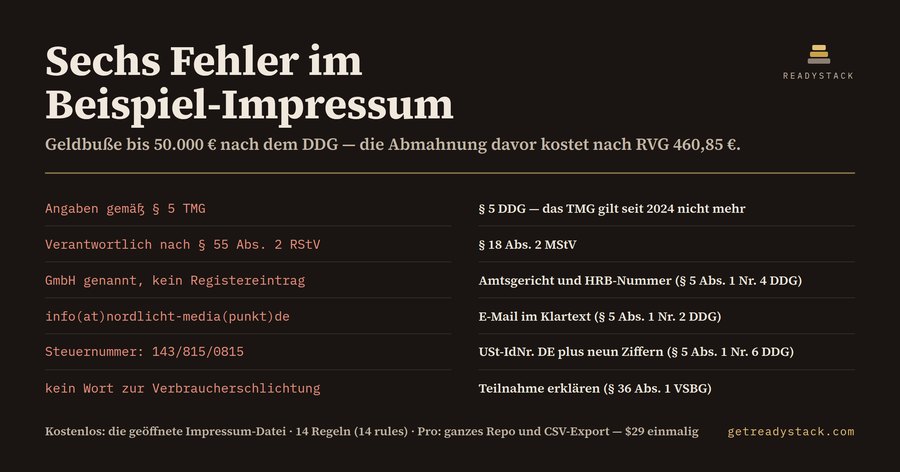
Prüft Impressum-Dateien im Editor gegen § 5 DDG, § 18 Abs. 2 MStV und § 36 VSBG
Install
npx @readystack/impressum-check-ddg-de file
Node 18+. The same 14 rules as the VS Code extension, from a terminal or CI.
Free
- Prüft die im Editor geöffnete Impressum-Datei gegen alle 14 Regeln und meldet jeden Treffer mit Zeilennummer und Norm. In der mitgelieferten Beispieldatei sind es 6 Treffer: § 5 TMG statt § 5 DDG, § 55 RStV statt § 18 Abs. 2 MStV, fehlendes Handelsregister, verschleierte E-Mail, Steuernummer statt USt-IdNr., fehlender VSBG-Hinweis.
--rules lists every rule
With a licence ($29 once)
- Prüft alle Impressum-Dateien eines Workspace in einem Durchlauf und exportiert den Befund als CSV-Nachweis für die Akte. $29 einmalig, ein Lizenzschlüssel pro Person oder Team-Sitzplatz, 7 Tage volle Rückerstattung.
@readystack/impressum-check-ddg-de --dir ./templates --report html --out report.html
Eine Abmahnung wegen fehlender Pflichtangaben kostet nach § 13 Abs. 1 RVG bei Gegenstandswert 5.000 € eine 1,3-Geschäftsgebühr von 460,85 € (1,0-Gebühr 354,50 €, Nr. 2300 VV RVG); § 33 Abs. 2 Nr. 1 i.V.m. Abs. 6 Nr. 3 DDG erlaubt eine Geldbuße bis 50.000 €.
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "impressum-check-ddg-de": { "command": "npx", "args": ["-y", "@readystack/impressum-check-ddg-de", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Impressum-Check DE: Pflichtangaben
  run: npx -y @readystack/impressum-check-ddg-de --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/impressum-check-ddg-de --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Get a licence



