労務書類 保存期間チェック
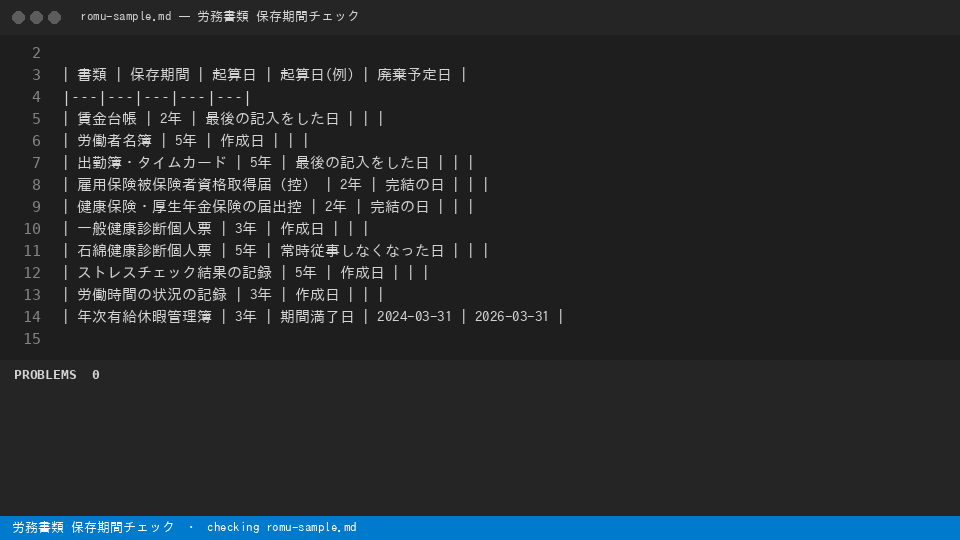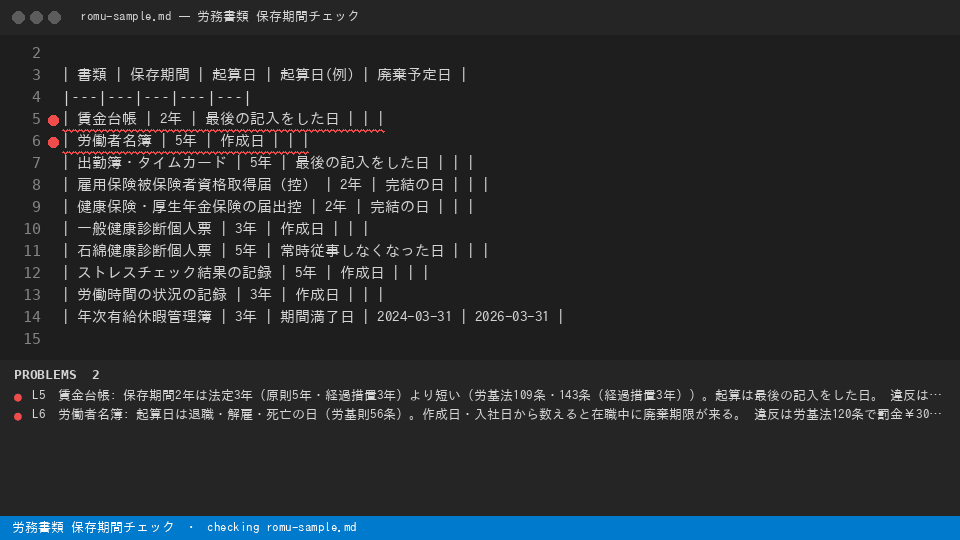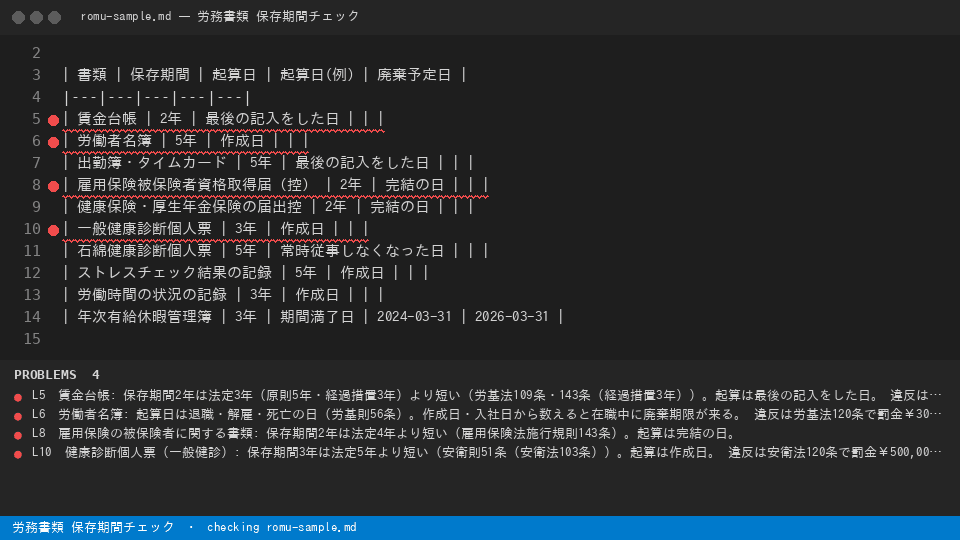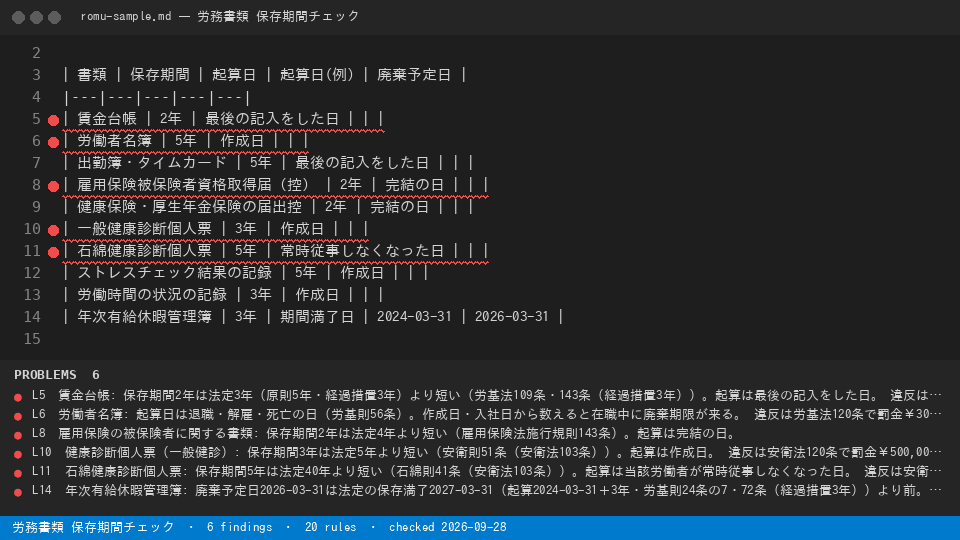
法定帳簿の保存期間を文書保存期間表で検査 — 労基法109条・安衛則51条・石綿則41条・雇用保険法施行規則143条・健保則34条(20 rules)
Install
npx @readystack/romu-hozon-kikan-lint-jp file
Node 18+. The same 20 rules as the VS Code extension, from a terminal or CI.
Free
- 開いている保存期間表1枚を検査し、法定年数より短い行・起算日の誤り・早すぎる廃棄予定日を行番号と条文つきで示す(キー不要)。
--rules lists every rule
With a licence ($29 once)
- ワークスペース内の規程・CSVを一括検査し、条文根拠と罰則つきの監査用レポートをMarkdown/CSVで書き出す。
@readystack/romu-hozon-kikan-lint-jp --dir ./templates --report html --out report.html
社労士の顧問契約は小規模事業所でも月額¥20,000前後が一般的な相場。
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "romu-hozon-kikan-lint-jp": { "command": "npx", "args": ["-y", "@readystack/romu-hozon-kikan-lint-jp", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: 労務書類 保存期間チェック
  run: npx -y @readystack/romu-hozon-kikan-lint-jp --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/romu-hozon-kikan-lint-jp --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Get a licence



