Tailwind v4 Upgrade Blocker Lint
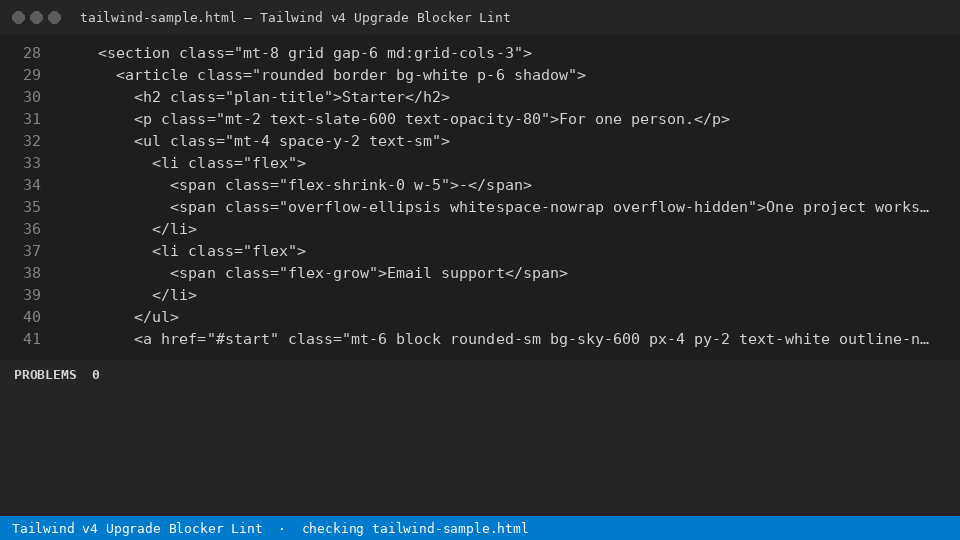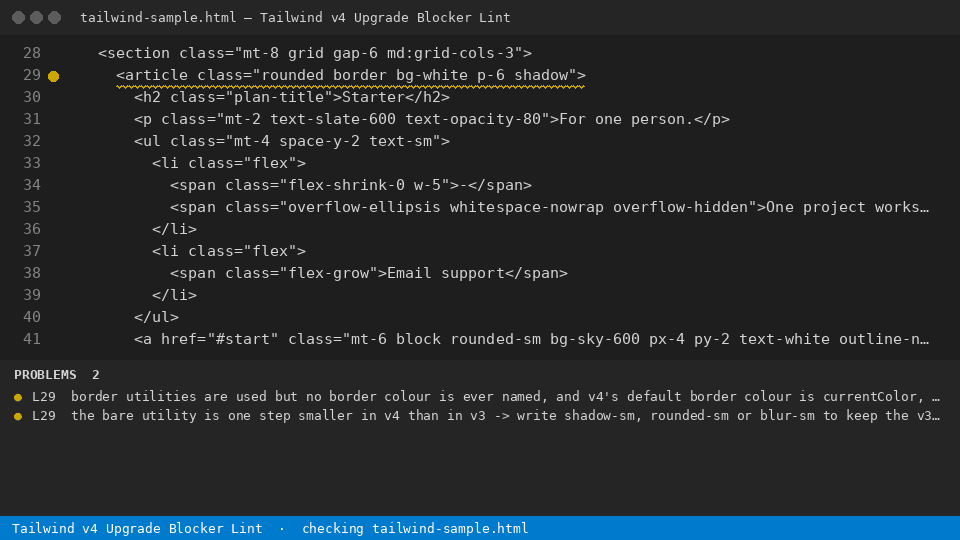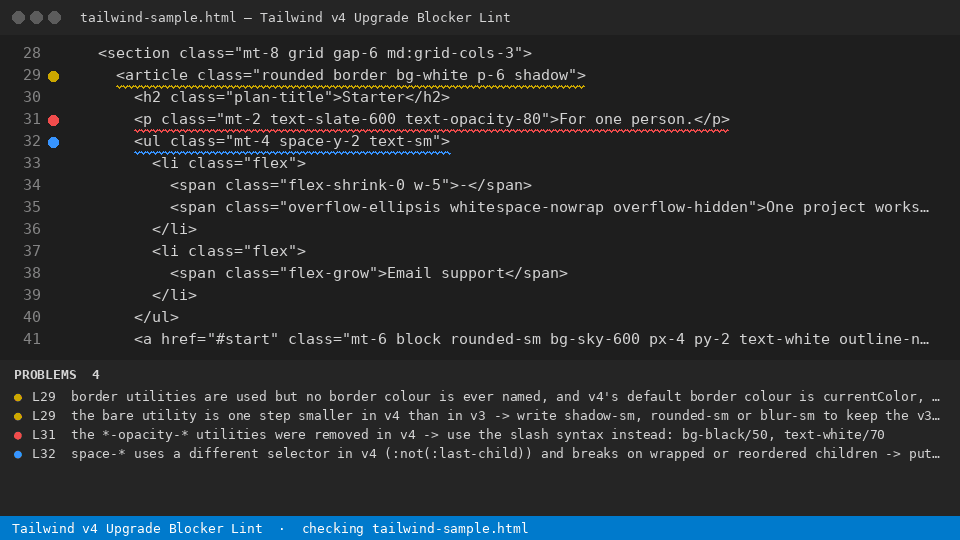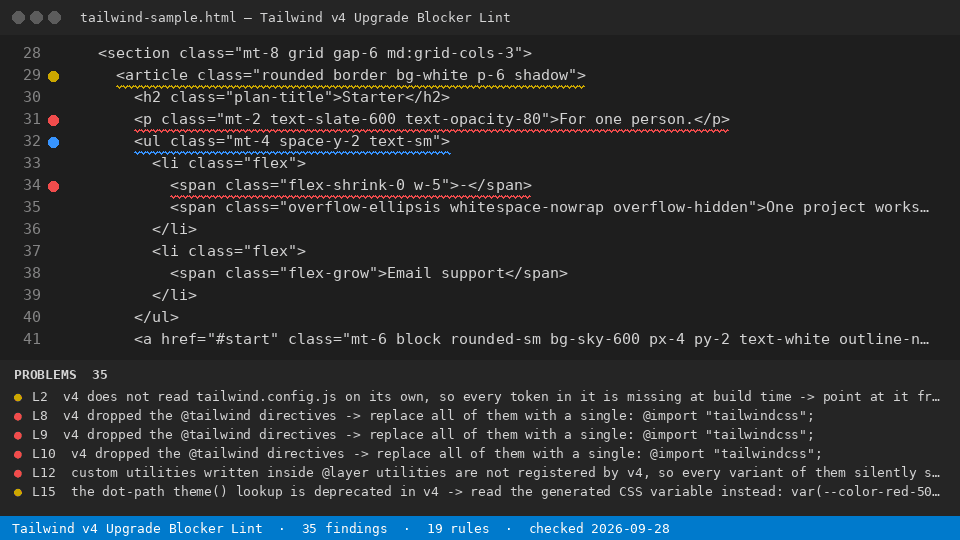
19 rules that find the Tailwind v3 syntax Tailwind v4 removed or silently redefined, in the file you have open, with the v4 replacement on the same line.
Install
npx @readystack/tailwind-v4-upgrade-blocker-lint file
Node 18+. The same 19 rules as the VS Code extension, from a terminal or CI.
Free
- Scan the file you have open and list every v3 construct v4 removed or silently redefined, with the line number and the v4 replacement
--rules lists every rule
With a licence ($29 once)
- Scan every file in the workspace in one command and write a dated Markdown migration report with a per-file count you can hand to your team
@readystack/tailwind-v4-upgrade-blocker-lint --dir ./templates --report html --out report.html
A front-end contractor sweeping the same codebase by hand bills 60-120 an hour.
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "tailwind-v4-upgrade-blocker-lint": { "command": "npx", "args": ["-y", "@readystack/tailwind-v4-upgrade-blocker-lint", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Tailwind v4 Upgrade Blocker Lint
  run: npx -y @readystack/tailwind-v4-upgrade-blocker-lint --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/tailwind-v4-upgrade-blocker-lint --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Get a licence



