Laravel Lang Compromised with RCE Backdoor Across 700+ Versions
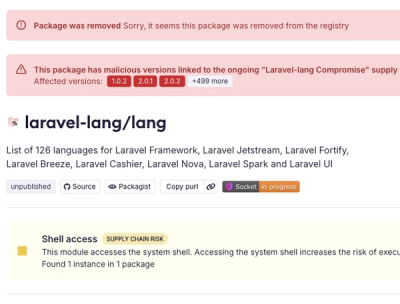
Laravel Lang packages were compromised with an RCE backdoor across hundreds of versions, exposing cloud, CI/CD, and developer secrets.
By Socket Research Team - May 23, 2026
Supply Chain Attack Campaign
A severe supply chain attack has compromised the PHP/Laravel ecosystem by poisoning approximately 700 versions of community-maintained laravel-lang packages (such as lang, http-statuses, attributes, and actions) via GitHub tag manipulation. Once a compromised package is installed, an autoloaded backdoor executes on every PHP request to silently fetch a highly sophisticated, cross-platform second-stage payload from an attacker-controlled server.
This payload acts as an aggressive information stealer designed to systematically harvest and exfiltrate a massive array of sensitive data from developer machines and production servers, including cloud provider keys, Kubernetes service accounts, CI/CD pipeline secrets, password manager vaults, browser session tokens, and cryptocurrency wallets. To maximize stealth, the malware uses a per-host marker to run only once, disables TLS network verification, and employs robust anti-forensic techniques to self-delete after exfiltration, making this a critical incident that requires the immediate isolation of affected environments and comprehensive secret rotation.
Ecosystems: composer
Laravel Lang packages were compromised with an RCE backdoor across hundreds of versions, exposing cloud, CI/CD, and developer secrets.