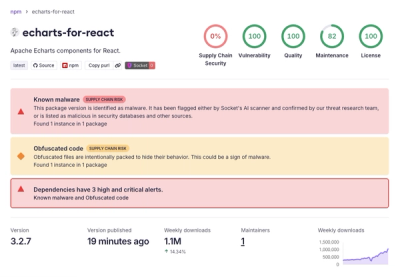
Mini Shai-Hulud Hits @antv Ecosystem, 639 Compromised npm Package Versions
Active npm supply chain attack compromises @antv packages in a fast-moving malicious publish wave tied to Mini Shai-Hulud.
By Socket Research Team - May 19, 2026
Supply Chain Attack Campaign
Since April 29, 2026, an ongoing supply chain campaign self-branded "Mini Shai-Hulud" has compromised packages across both npm and PyPI using a shared payload architecture: a preinstall or import-time hook downloads a platform-specific Bun runtime from GitHub Releases and executes a ~11.7 MB obfuscated JavaScript credential stealer (execution.js / router_runtime.js) that exfiltrates developer and CI/CD secrets through attacker-created GitHub repositories tagged with the description "A Mini Shai-Hulud has Appeared." Confirmed compromises include four SAP Cloud Application Programming (CAP) and Cloud MTA Build Tool npm packages (mbt@1.2.48, @cap-js/db-service@2.10.1, @cap-js/postgres@2.2.2, @cap-js/sqlite@2.2.2), intercom-client@7.0.4 on npm, and lightning versions 2.6.2 and 2.6.3 on PyPI. The payload harvests SSH keys, cloud credentials (AWS, Azure, GCP, Kubernetes), Vault and GitHub tokens, npm tokens, and AI-tool configuration files; encrypts results with RSA-OAEP-4096 and AES-256-GCM; self-propagates by republishing into packages reachable via stolen npm tokens; and persists through .claude/settings.json SessionStart hooks and .vscode/tasks.json. Socket assesses with high confidence that the campaign is linked to TeamPCP, the actor behind recent compromises of Bitwarden CLI, Checkmarx KICS/AST, Aqua Security Trivy, Telnyx, and LiteLLM.
Ecosystems: npm, pypi
Active npm supply chain attack compromises @antv packages in a fast-moving malicious publish wave tied to Mini Shai-Hulud.
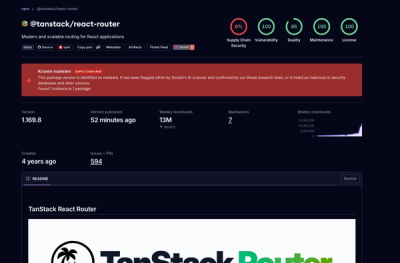
Socket detected 84 compromised TanStack npm package artifacts modified with suspected CI credential-stealing malware.
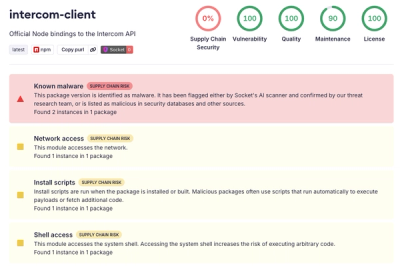
Compromised intercom-client@7.0.4 npm package is tied to the ongoing Mini Shai-Hulud worm attack targeting developer and CI/CD secrets.
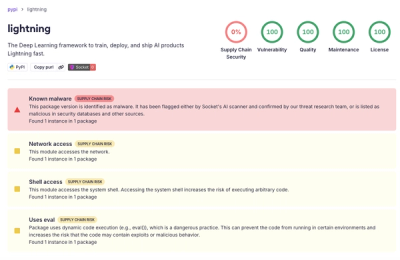
Socket detected a malicious supply chain attack on PyPI package lightning versions 2.6.2 and 2.6.3, which execute credential-stealing malware on import.
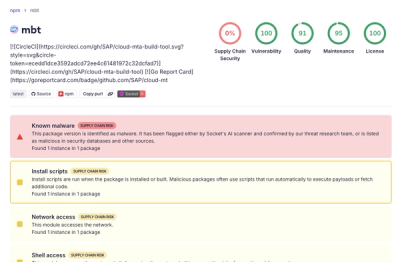
Compromised SAP CAP npm packages download and execute unverified binaries, creating urgent supply chain risk for affected developers and CI/CD environments.