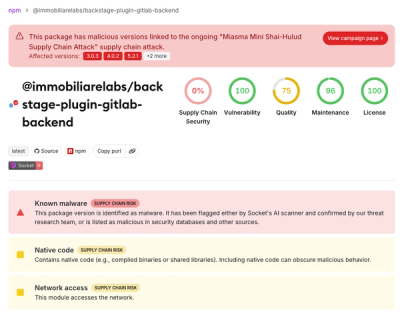
Miasma Mini Shai-Hulud Hits ImmobiliareLabs npm Packages
Miasma Mini Shai-Hulud hits @immobiliarelabs Backstage plugins, targeting GitLab and LDAP auth packages on npm.
By Socket Research Team - Jun 26, 2026
Supply Chain Attack Campaign
Miasma is the latest Mini Shai-Hulud npm supply chain wave, first observed in compromised Red Hat Cloud Services packages before spreading to additional victims, including the Vapi server SDK and packages in the ai-sdk-ollama, autotel, awaitly, executable-stories, node-env-resolver, and wrangler-deploy ecosystems. The campaign uses TeamPCP-linked tradecraft to turn package installation into credential theft and propagation: obfuscated install-time payloads, Bun-based staging, GitHub Actions runner secret extraction, npm and cloud credential harvesting, encrypted GitHub dead-drop exfiltration, and automated package compromise. The name “Miasma” comes from threat actor-created repository descriptions such as “Miasma: The Spreading Blight”, matching the campaign’s self-spreading behavior and Greek mythology-themed variant language.
Ecosystems: npm, pypi
Miasma Mini Shai-Hulud hits @immobiliarelabs Backstage plugins, targeting GitLab and LDAP auth packages on npm.
Mini Shai-Hulud expands into the Go ecosystem after hitting LeoPlatform npm packages and targeting GitHub Actions workflows.
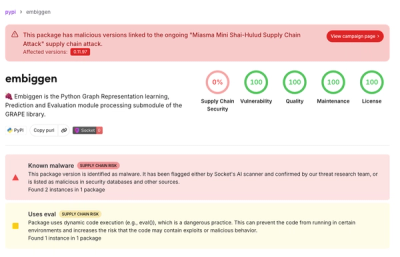
Newer packages in this compromise use native extensions and .pth loaders to execute JavaScript stealers in developer environments.
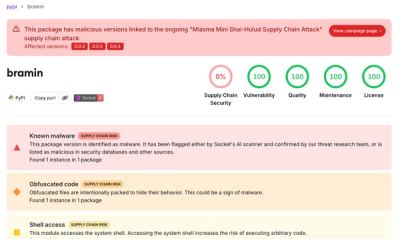
Socket found 37 malicious PyPI wheels that abuse Python startup hooks to launch a Bun-powered credential stealer tied to Mini Shai-Hulud/Miasma.
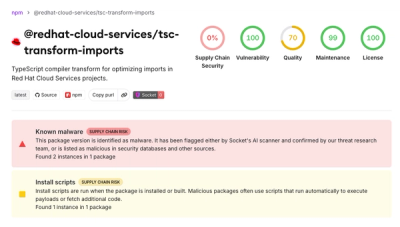
A mini Shai-Hulud campaign compromised Red Hat Cloud Services npm packages to steal developer and CI/CD secrets during installation.