Agentforce Action Audit
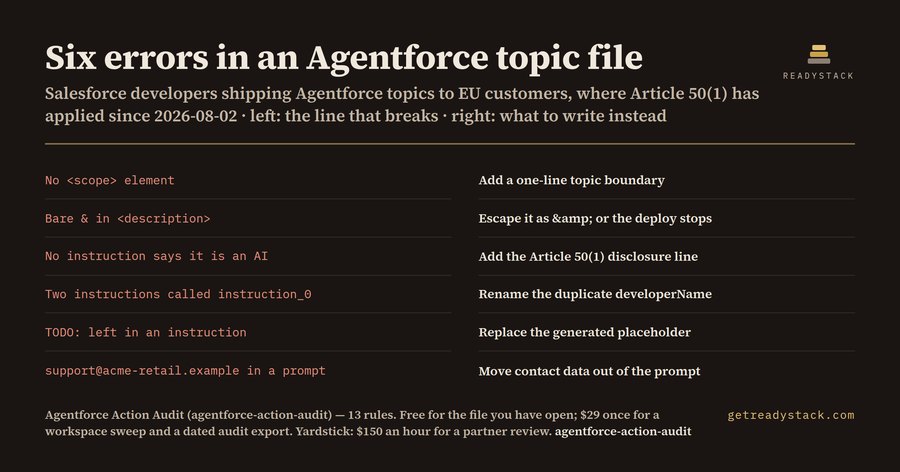
13 rules on a Salesforce Agentforce topic file, before the deploy and before Article 50
Install
npx @readystack/agentforce-action-audit file
Node 18+. The same 13 rules as the VS Code extension, from a terminal or CI.
Free
- Audit the Agentforce topic metadata file you have open and get every deploy blocker with its line number.
--rules lists every rule
With a licence ($29 once)
- Sweep every genAiPlugin and genAiPlannerBundle in the workspace in one run and export a dated AGENTFORCE-AUDIT.md for the change request.
@readystack/agentforce-action-audit --dir ./templates --report html --out report.html
A Salesforce partner bills metadata review at about $150 an hour; one topic file takes roughly 20 minutes to read by hand.
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "agentforce-action-audit": { "command": "npx", "args": ["-y", "@readystack/agentforce-action-audit", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Agentforce Action Audit
  run: npx -y @readystack/agentforce-action-audit --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/agentforce-action-audit --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Get a licence



