CBPR+ Structured Address Lint
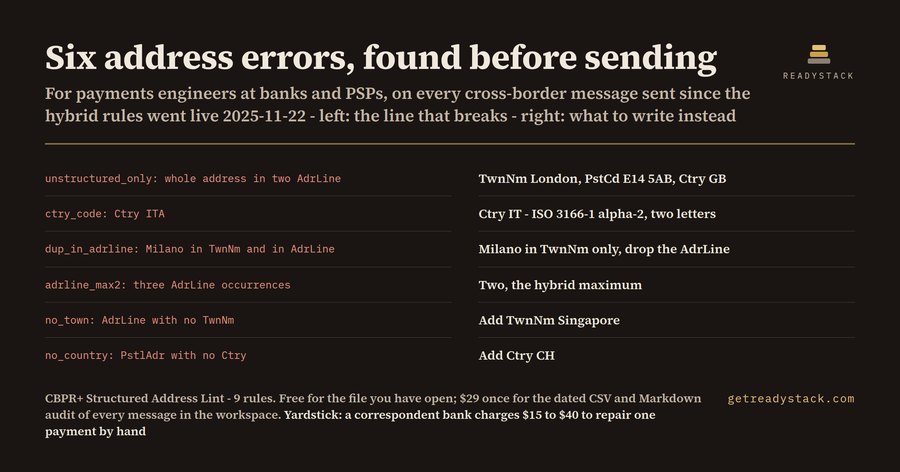
Find the ISO 20022 postal addresses your correspondent bank will repair by hand, before you send the message
Install
npx @readystack/cbpr-address-lint file
Node 18+. The same 9 rules as the VS Code extension, from a terminal or CI.
Free
- Lints any ISO 20022 XML in your editor against all 9 CBPR+ postal-address rules, hybrid rules live since 2025-11-22 and the unstructured cutover deferred 2026-08-27 - 6 errors and 3 warnings - and names each failing PstlAdr block on its own line. On the sample dirty.xml that is 13 findings, 9 errors and 4 warnings, across all 4 party address blocks; on clean.xml it is 0. The 6 errors: (1) unstructured_only, address held only in AdrLine with no TwnNm and no Ctry; (2) no_country, structured block with no Ctry; (3) no_town, hybrid block with no TwnNm; (4) dup_in_adrline, a value in both a dedicated element and an AdrLine; (5) adrline_max2, more than 2 AdrLine occurrences; (6) ctry_code, a Ctry that is not 2 upper-case letters. The 3 warnings: adrline_70, charset, bldgnb_in_strtnm.
--rules lists every rule
With a licence ($29 once)
- Exports a dated CBPR+ address audit file, CSV and Markdown, covering every ISO 20022 message in the workspace, with the rule citation per finding, so the evidence leaves the editor as a file you can hand to your correspondent bank, your migration programme or your auditor. $29 once, one licence key per person or CI seat.
@readystack/cbpr-address-lint --dir ./templates --report html --out report.html
A correspondent bank charges $15 to $40 to repair one cross-border payment by hand; the average fee for a rejected or repaired payment is reported at about $12.
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "cbpr-address-lint": { "command": "npx", "args": ["-y", "@readystack/cbpr-address-lint", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: CBPR+ Structured Address Lint
  run: npx -y @readystack/cbpr-address-lint --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/cbpr-address-lint --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Get a licence



