Crypto Export Notice Lint (EAR 742.15)
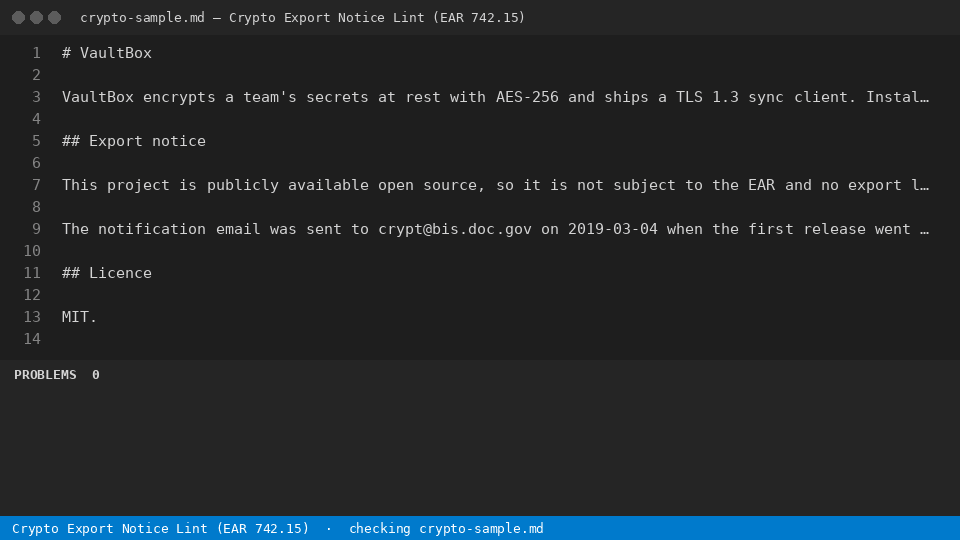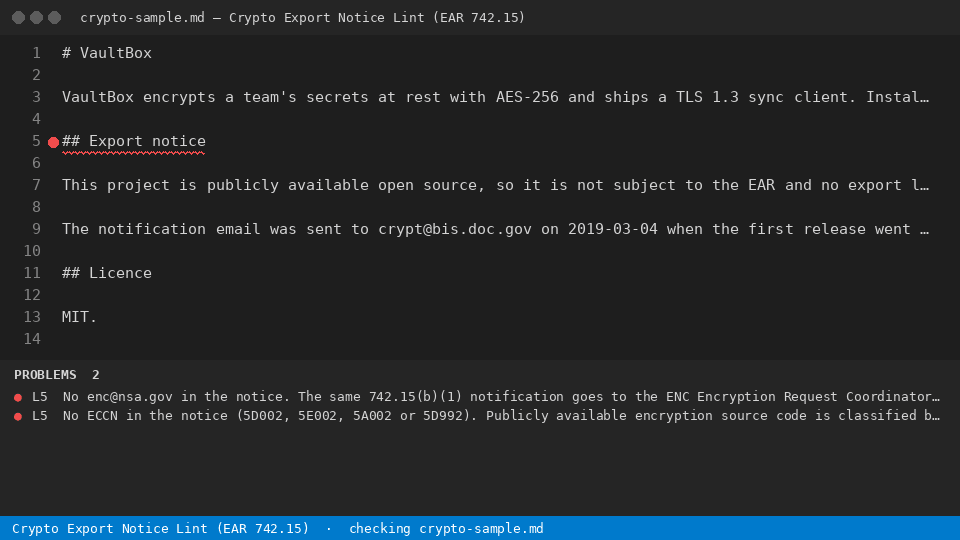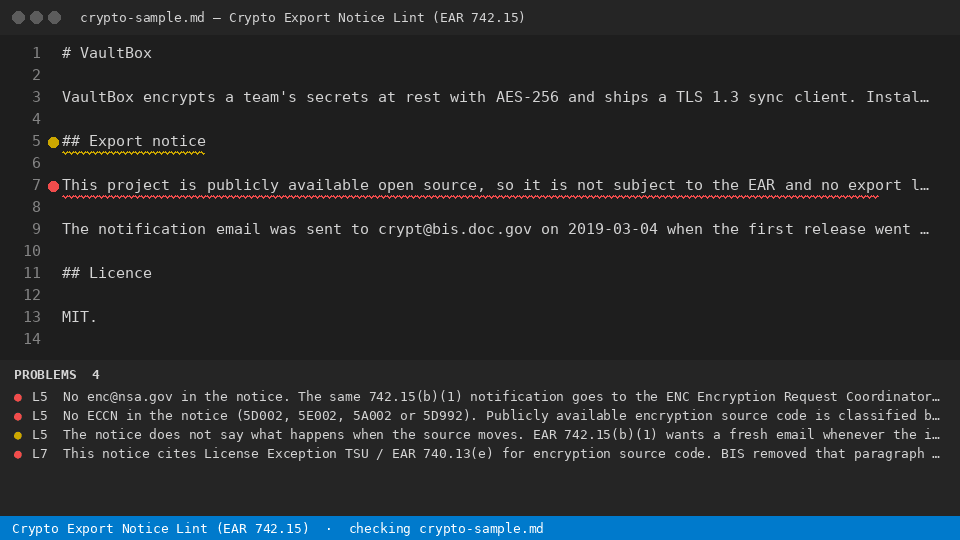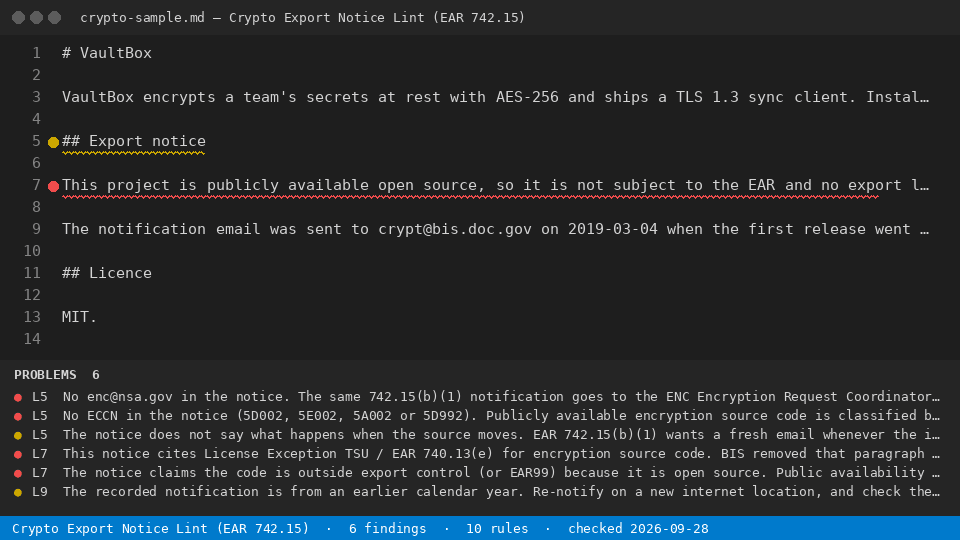
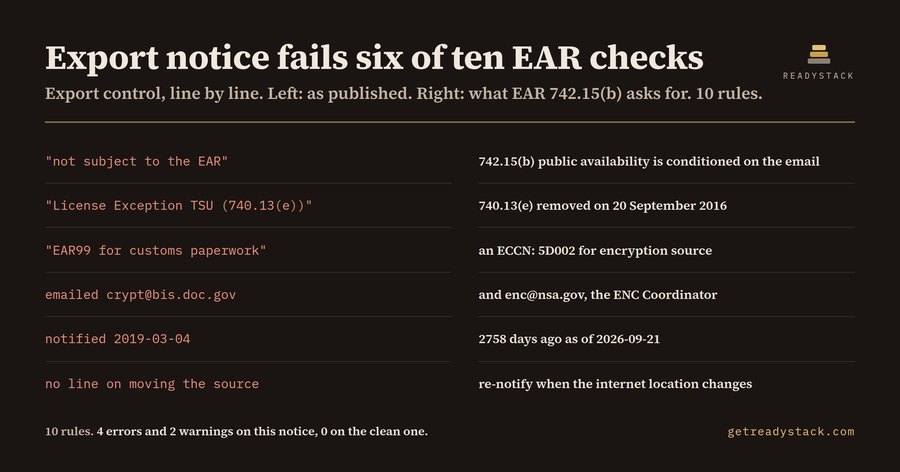
Ten checks on the export paragraph of a repository that ships encryption
Install
npx @readystack/crypto-export-notice-lint file
Node 18+. The same 10 rules as the VS Code extension, from a terminal or CI.
Free
- Run all 10 checks on the README or EXPORT notice open in the editor and get the findings in the Problems panel — the file is finished without a key.
--rules lists every rule
With a licence ($29 once)
- Sweep every Markdown file in the repository and write a dated cryptoExport-report.md you keep and hand over: scope and ownership, not a limit on the free check.
@readystack/crypto-export-notice-lint --dir ./templates --report html --out report.html
US export-control counsel is commonly quoted at 300-600 USD per hour, and a release review is not billed in minutes.
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "crypto-export-notice-lint": { "command": "npx", "args": ["-y", "@readystack/crypto-export-notice-lint", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Crypto Export Notice Lint (EAR 742.15)
  run: npx -y @readystack/crypto-export-notice-lint --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/crypto-export-notice-lint --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Get a licence



