Impressum & Shop-Pflichtangaben Lint (DE)
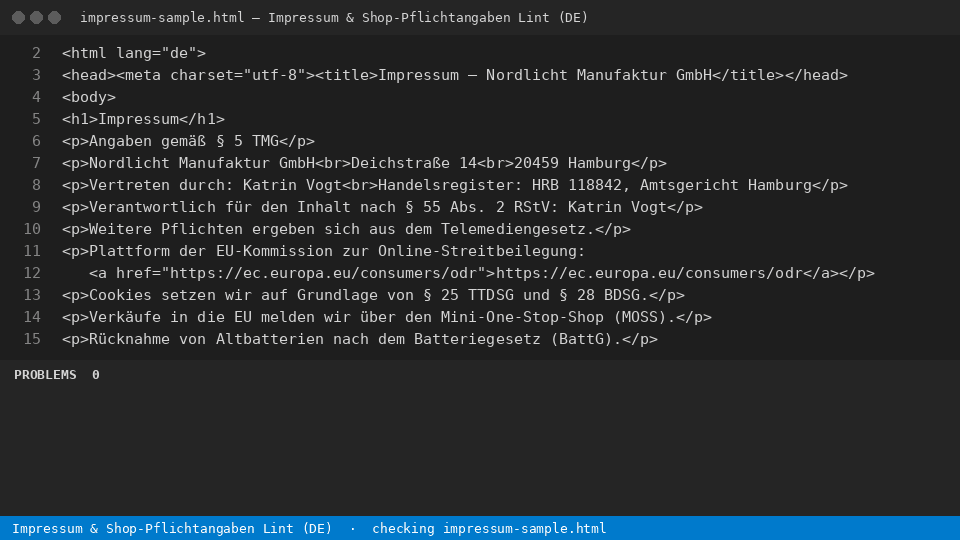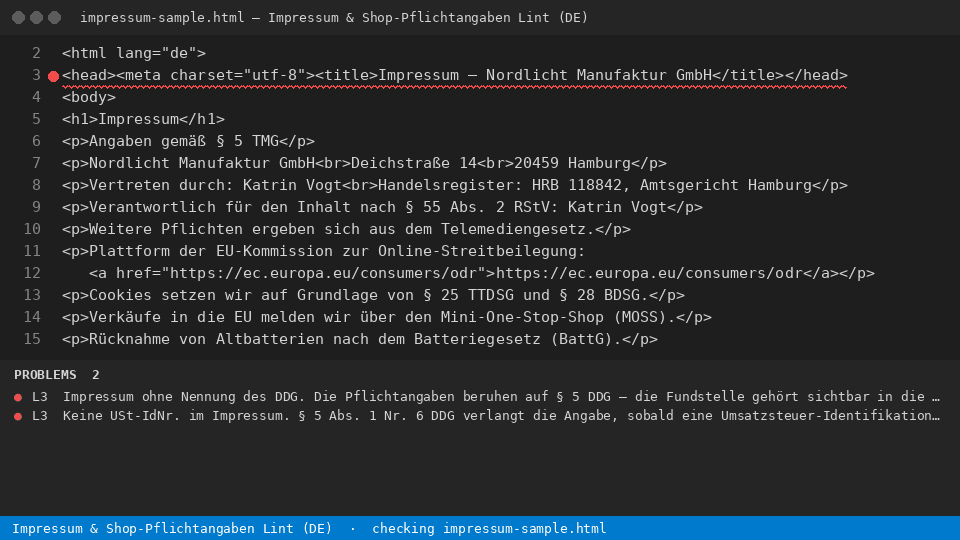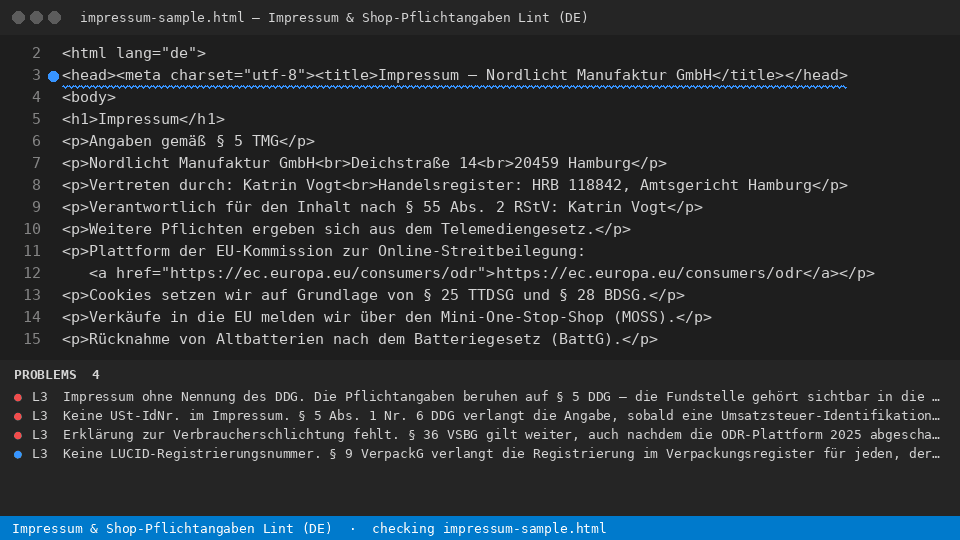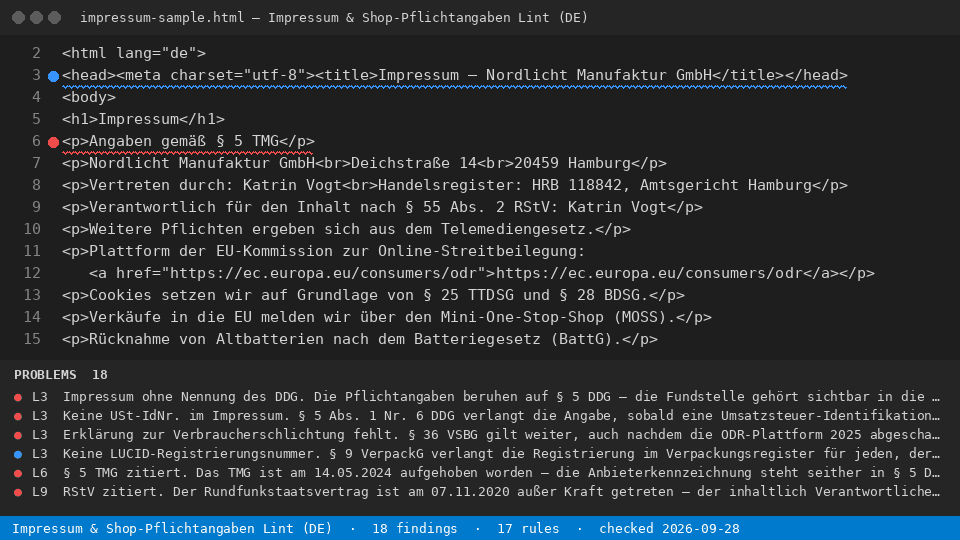
17 Regeln mit Stichtag für Impressum, Footer und Shop-Templates im Repository
Install
npx @readystack/impressum-lint-de file
Node 18+. The same 17 rules as the VS Code extension, from a terminal or CI.
Free
- Prüft jede Datei und den ganzen Workspace und zeigt jede veraltete Fundstelle und jede fehlende Pflichtangabe mit Zeile, geltender Norm und Stichtag.
--rules lists every rule
With a licence ($29 once)
- Exportiert das datierte Prüfprotokoll als Markdown und JSON zum Mitnehmen in Akte, CI-Pipeline und Mandantendokumentation.
@readystack/impressum-lint-de --dir ./templates --report html --out report.html
Anwaltliche Rechtstext-Schutzpakete für Onlineshops laufen dauerhaft ab 8,25 € bis 15 € im Monat (onwalt ab 8,25 €, eRecht24 ab 15,00 €, Flyeralarm Digital 12,90 € netto bei 12 Monaten Laufzeit).
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "impressum-lint-de": { "command": "npx", "args": ["-y", "@readystack/impressum-lint-de", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Impressum & Shop-Pflichtangaben Lint (DE)
  run: npx -y @readystack/impressum-lint-de --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/impressum-lint-de --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Get a licence



