

Security News
/Company News
Securing the Financial Frontier: How Capital One Uses Socket for Open Source Security
Capital One is partnering with Socket to proactively secure its open source supply chain.
By Sarah Gooding - Oct 01, 2026
@readystack/play-declaration-gap-lint
Advanced tools
15 checks that name every Play Console declaration your manifest opens
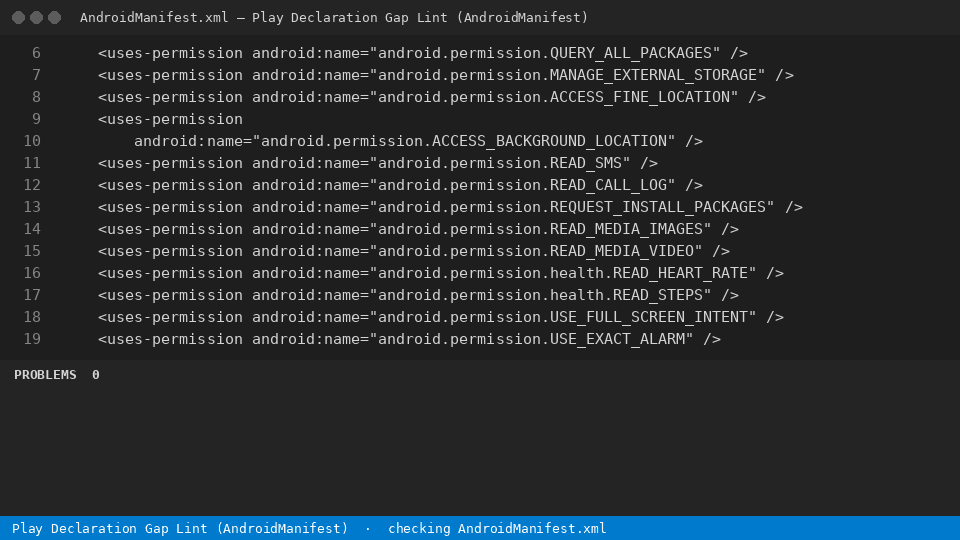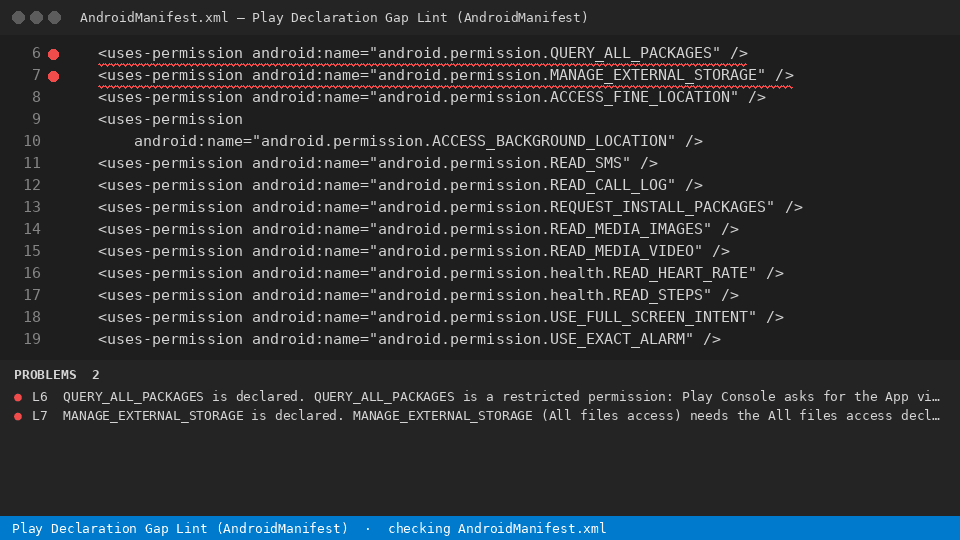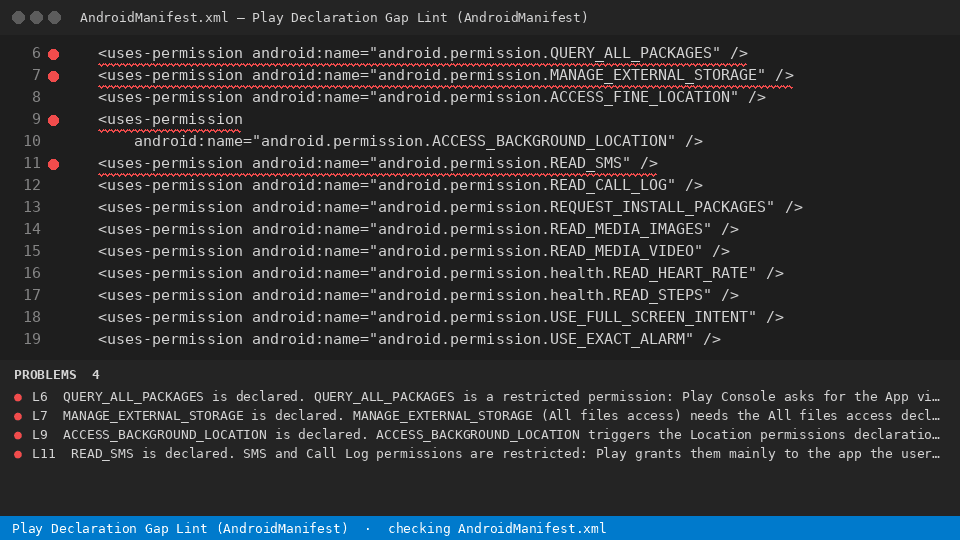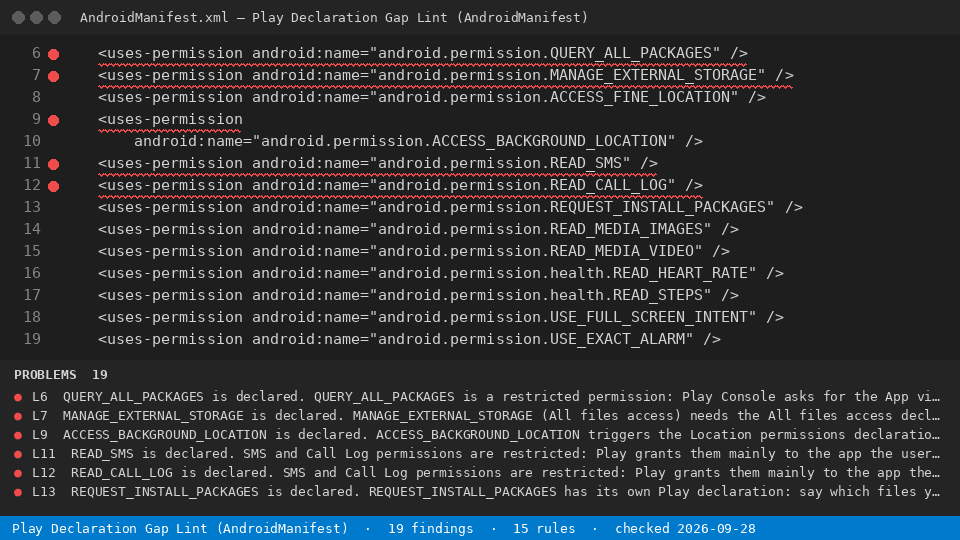
15 checks that name every Play Console declaration your manifest opens
npx @readystack/play-declaration-gap-lint file
Node 18+. The same 15 rules as the VS Code extension, from a terminal or CI.
--rules lists every rule@readystack/play-declaration-gap-lint --dir ./templates --report html --out report.html
A freelance Android release engineer bills $60-$120 an hour; reading a multi-module app's manifests against every current Play declaration is most of a working day
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "play-declaration-gap-lint": { "command": "npx", "args": ["-y", "@readystack/play-declaration-gap-lint", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
- name: Play Declaration Gap Lint (AndroidManifest)
  run: npx -y @readystack/play-declaration-gap-lint --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/play-declaration-gap-lint --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
FAQs
15 checks that name every Play Console declaration your manifest opens
The npm package @readystack/play-declaration-gap-lint receives a total of 370 weekly downloads. As such, @readystack/play-declaration-gap-lint popularity was classified as not popular.
We found that @readystack/play-declaration-gap-lint demonstrated a healthy version release cadence and project activity because the last version was released less than a year ago. It has 1 open source maintainer collaborating on the project.
Security News
/Company News
Capital One is partnering with Socket to proactively secure its open source supply chain.

Security News
Socket CTO Ahmad Nassri discusses how to keep AI agents from bypassing package blocks, limit credential access, and monitor their actions.

Security News
GPT-6 Astra tried to plant malicious code in simulated open source projects using fake GitHub accounts and deceptive PRs during an assigned CTF challenge.