security.txt Lint - RFC 9116 + CRA contact point
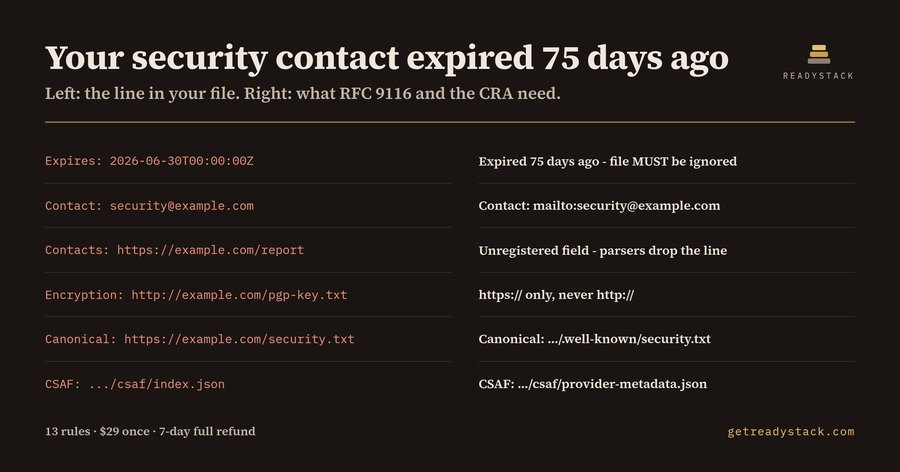
13 rules that decide whether a vulnerability report ever reaches you
Install
npx @readystack/security-txt-cra-lint file
Node 18+. The same 13 rules as the VS Code extension, from a terminal or CI.
Free
- Lint the security.txt you have open and see every RFC 9116 and CRA contact-point finding on its exact line.
--rules lists every rule
With a licence ($29 once)
- Scan every security.txt across the whole workspace in one pass and export a dated JSON report you keep for the audit file.
@readystack/security-txt-cra-lint --dir ./templates --report html --out report.html
A security consultant reviewing a disclosure contact and policy starts around $150 an hour
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "security-txt-cra-lint": { "command": "npx", "args": ["-y", "@readystack/security-txt-cra-lint", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence; the full sweep is free for 7 days). The agent gets every finding with the line number.
Use in CI
- name: security.txt Lint - RFC 9116 + CRA contact point
  run: npx -y @readystack/security-txt-cra-lint --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/security-txt-cra-lint --dir /work --ci)
Try the full run free for 7 days — no key needed. Then one licence, 7-day refund, no questions. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Get a licence



