Webfont License Audit
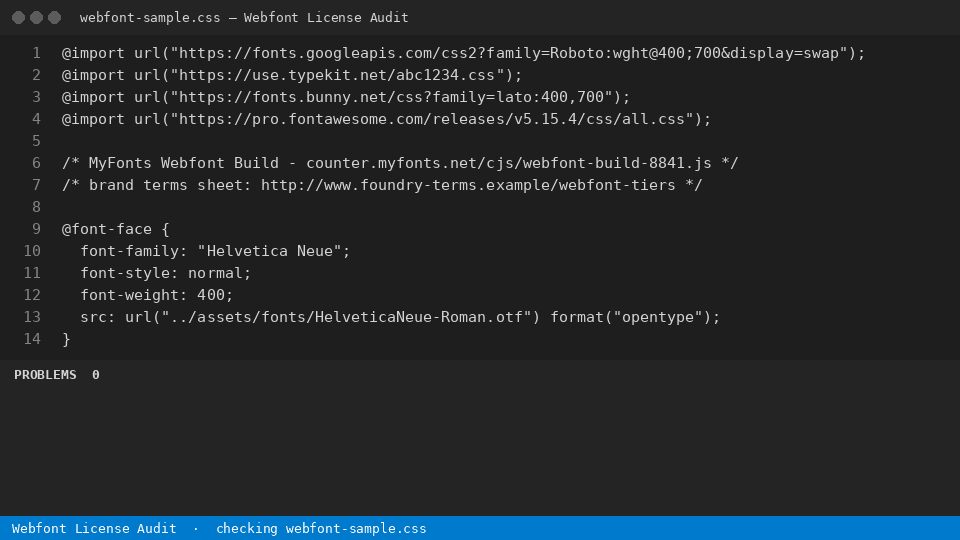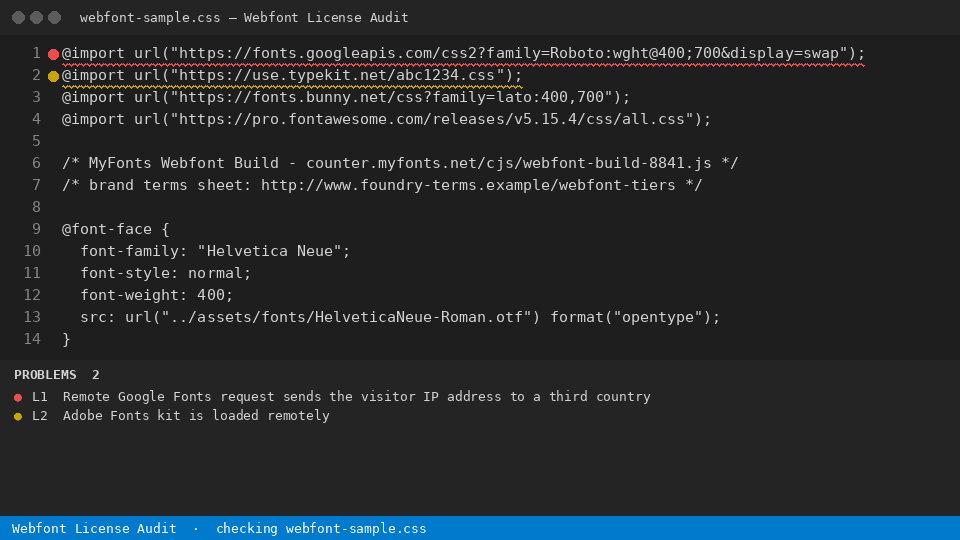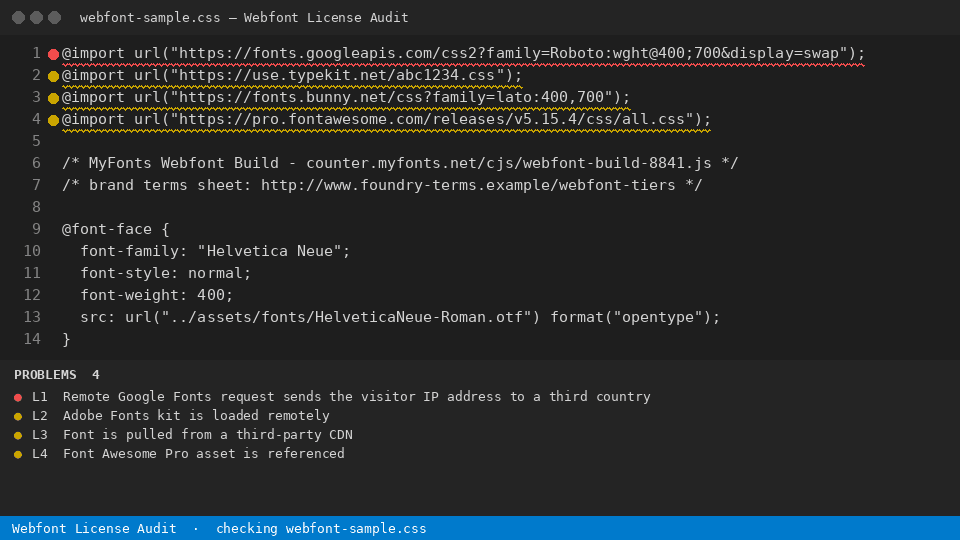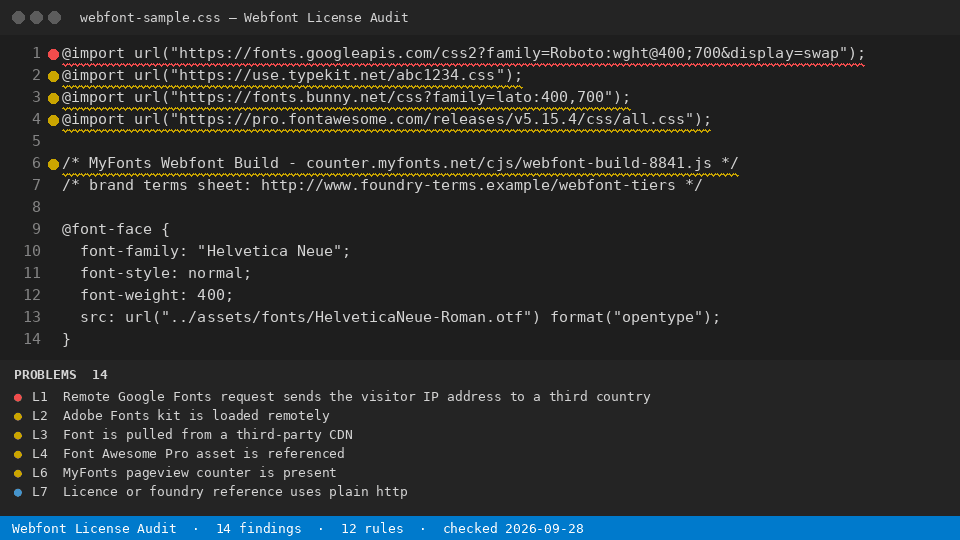
The 12 licence questions a foundry audit letter asks, run against your CSS
Install
npx @readystack/webfont-license-audit file
Node 18+. The same 12 rules as the VS Code extension, from a terminal or CI.
Free
- Scans every CSS, SCSS and LESS file in the workspace and lists each webfont licence risk with its rule id, severity and line number.
--rules lists every rule
With a licence ($29 once)
- Exports the whole finding list as a dated FONT-LICENSE-AUDIT.md plus CSV evidence pack you keep and hand to a foundry auditor or your own legal team.
@readystack/webfont-license-audit --dir ./templates --report html --out report.html
LG Muenchen I, 3 O 17493/20, 2022-01-20: 100 euro damages to one visitor for a remote Google Fonts call; a solicitor's reply bills by the hour.
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "webfont-license-audit": { "command": "npx", "args": ["-y", "@readystack/webfont-license-audit", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: Webfont License Audit
  run: npx -y @readystack/webfont-license-audit --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/webfont-license-audit --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Get a licence



