comiceditorial (cmed)
Comic publishing for coding agents. A zero-dependency CLI + MCP server for the
ComicEditorial platform — a multi-tenant "Substack for comic books". Create
comics, chapters and pages, author interactive (branching) stories, draft
panels with AI, and export to CBZ. As easy as git.
npm install -g comiceditorial
Quickstart
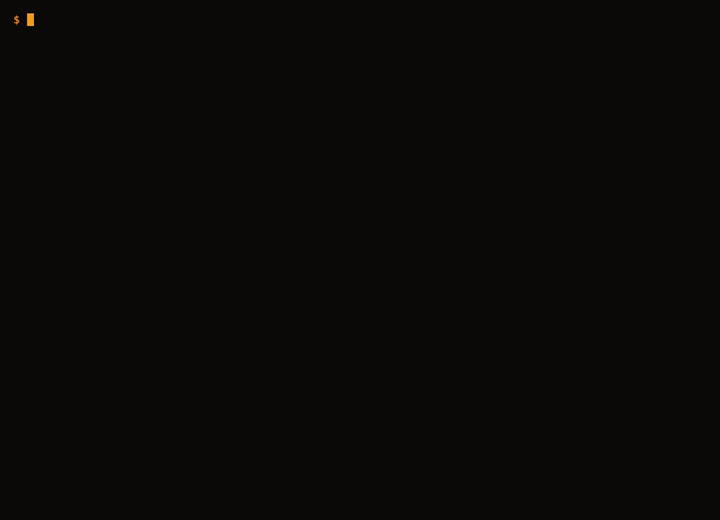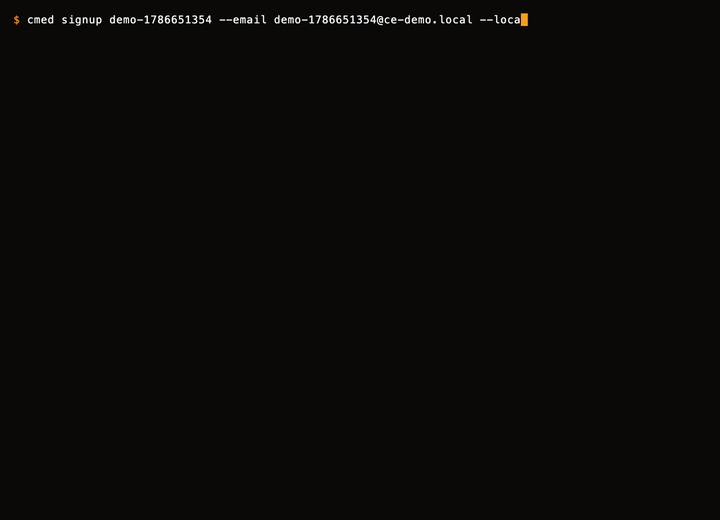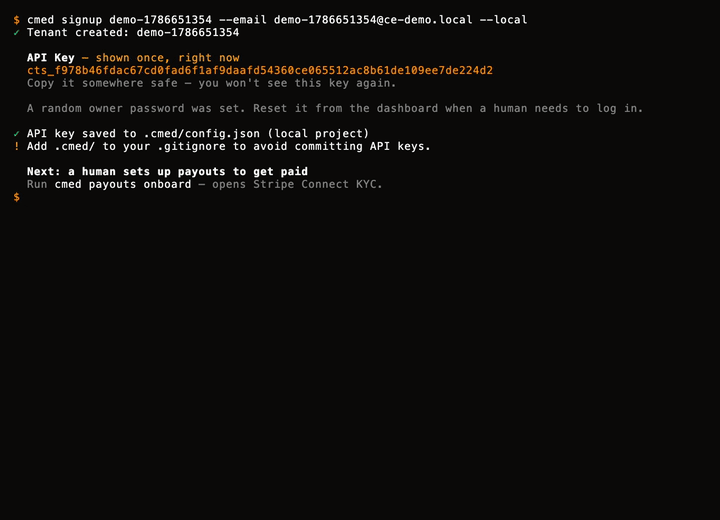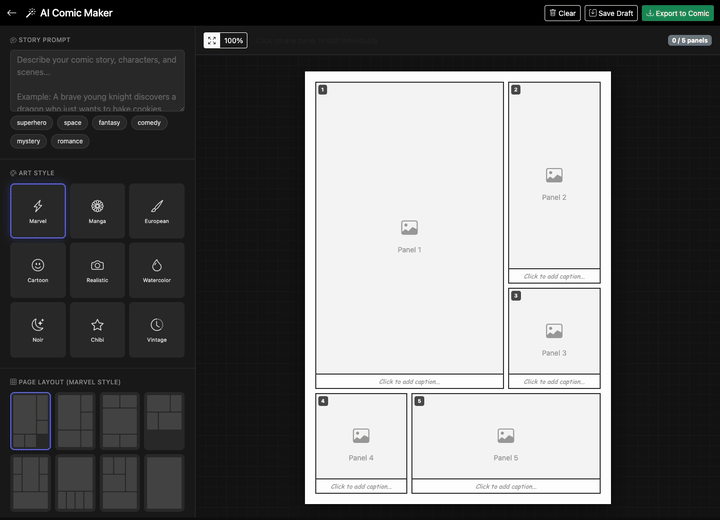
cmed signup my-studio --local
cmed me
cmed comic "My Hero" -g fantasy
cmed chapter create COMIC-ID "Chapter 1" --number 1
cmed comic status COMIC-ID published
cmed export cbz COMIC-ID --out out.cbz
Already have a cts_ key? cmed login --local --key cts_...
Run cmed init for an in-terminal quickstart, or cmed init --agent-schema
for the machine-readable command contract (JSON). Full reference: cmed --help.
Watch it work
Real cmed sessions and the ComicEditorial dashboard — click any clip for the
full video.
Sign up — an API key in seconds
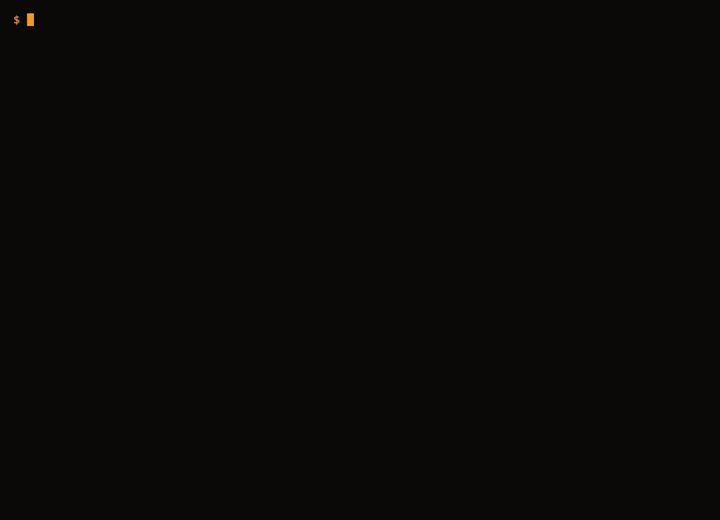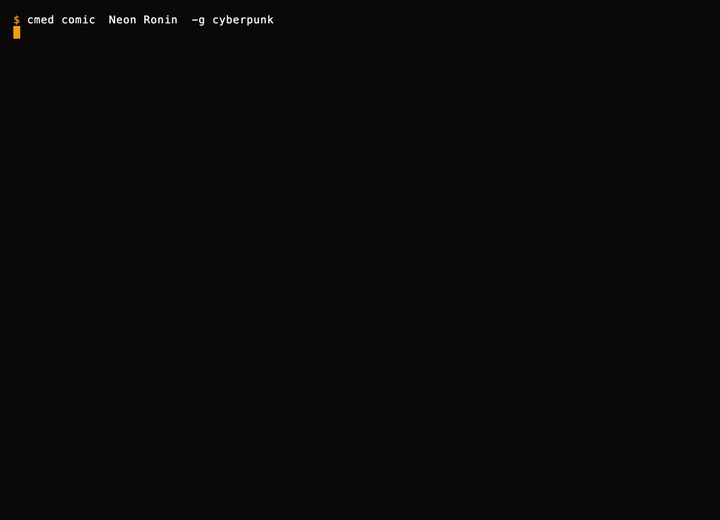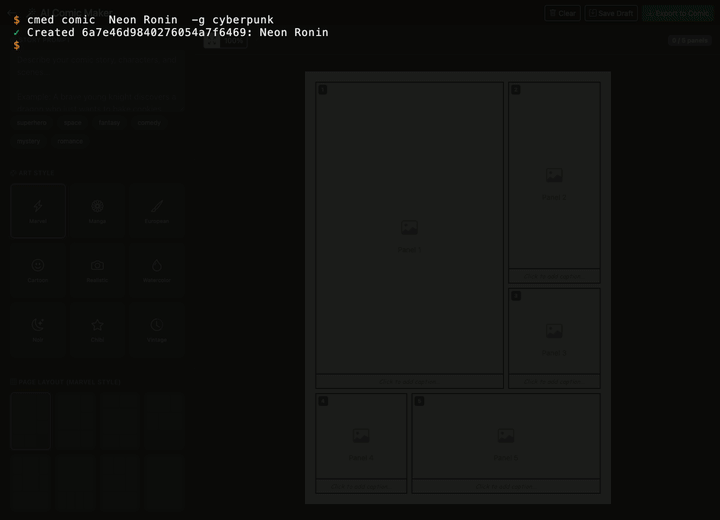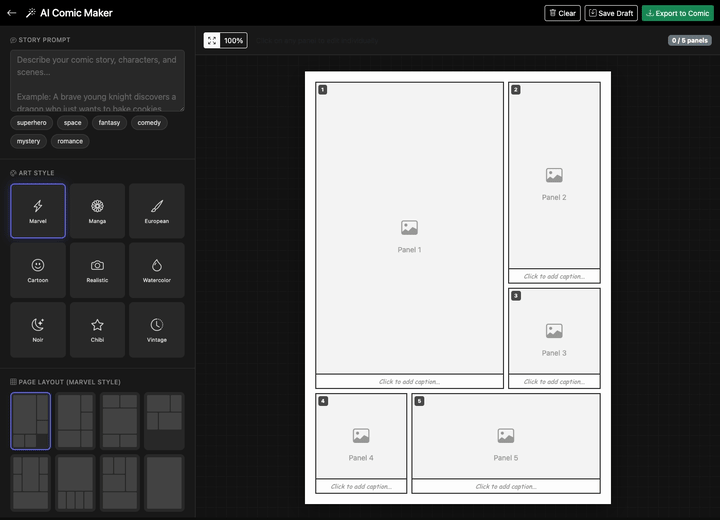
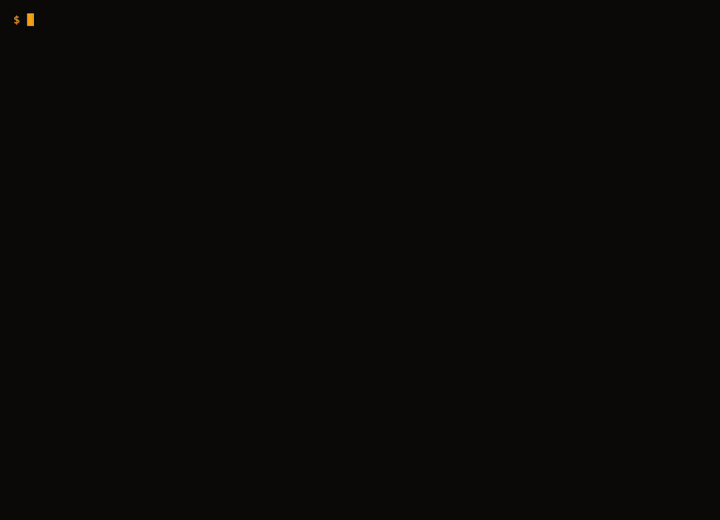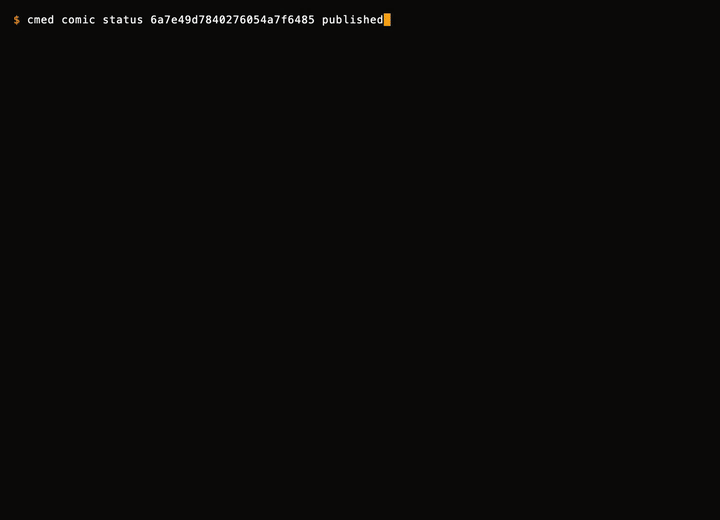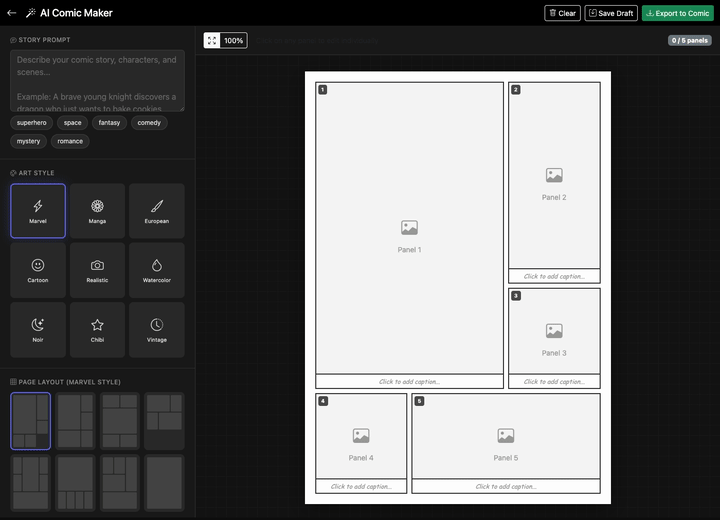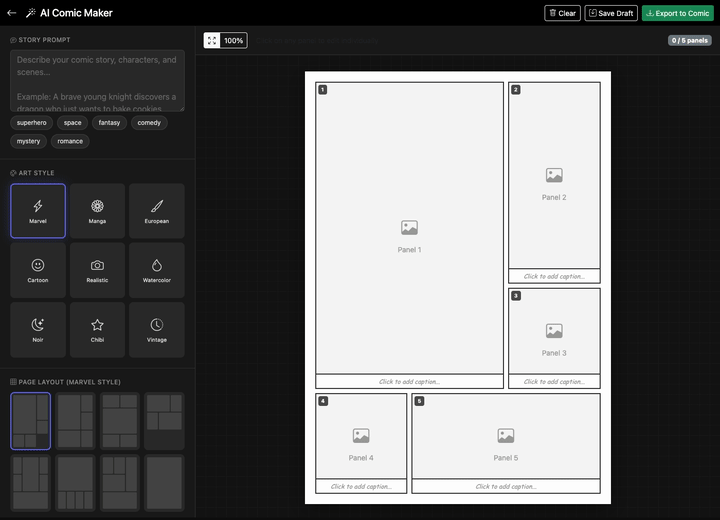
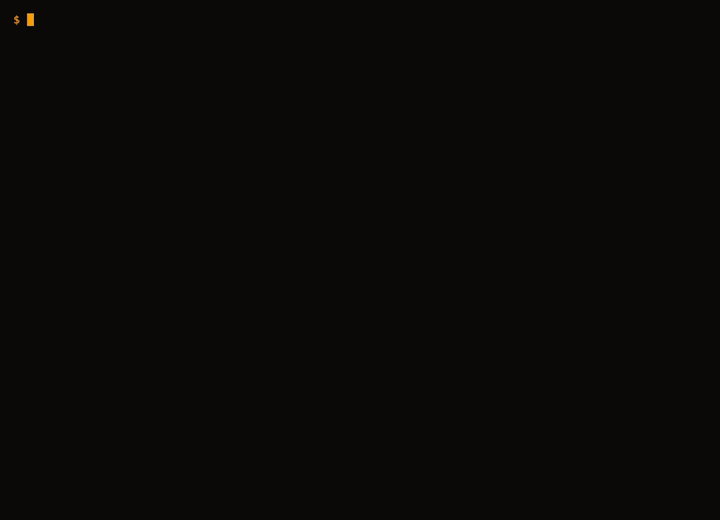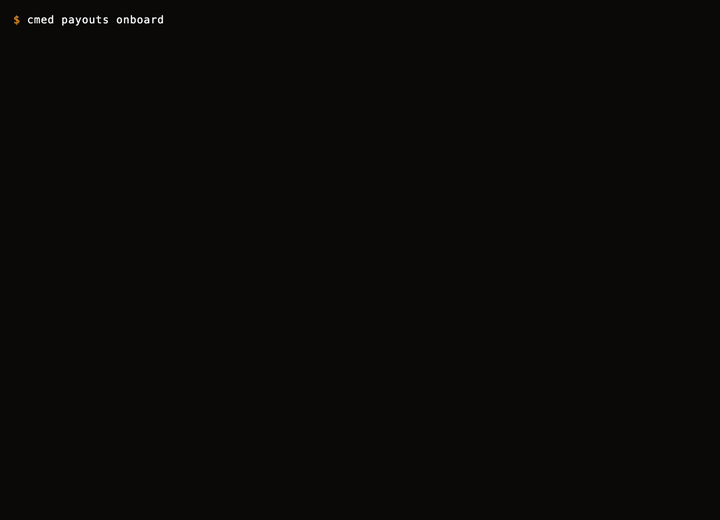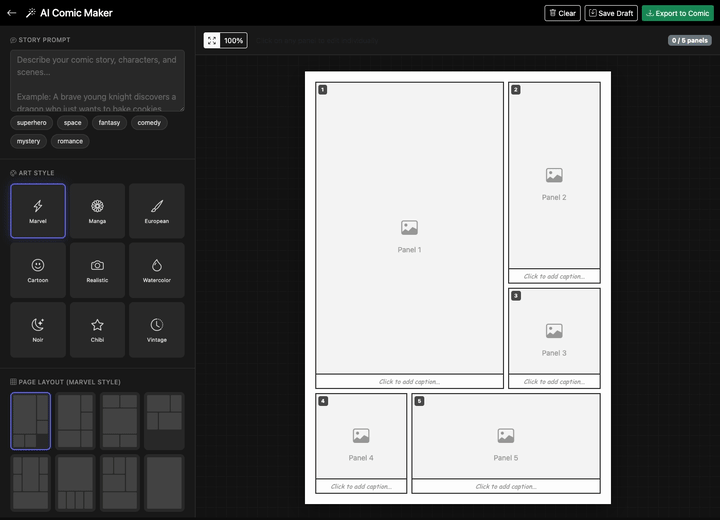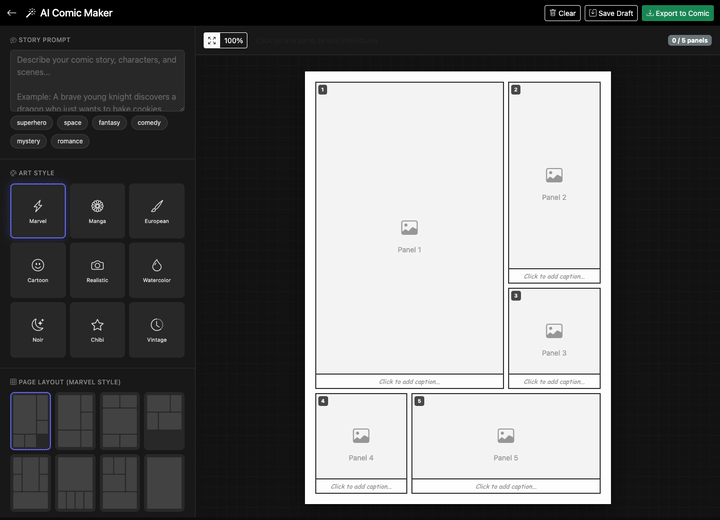
 | Create with AI — draft a comic from a prompt
 |
Publish — one command makes it live
 | Get paid — connect Stripe, readers pay you
 |
See the full tabbed demo at comic.tyga.studio.
Configuration
Priority: --key flag > CMED_API_KEY env > .cmed/config.json (project-local).
Base URL defaults to https://comic.tyga.studio (override with --api-url or
CMED_URL). Add .cmed/ to your .gitignore.
Commands
| Setup | signup, login, logout, me, config, key, init |
| Payouts | payouts, payouts onboard (Stripe Connect — get paid by readers) |
| Comics | comics, comic {show,create,update,status,cover,delete,stats} |
| Chapters | chapters COMIC-ID, chapter {show,create,update,delete,reorder} |
| Pages | pages CHAPTER-ID, page {delete,reorder} |
| Stories | stories, story {show,create,update,duplicate,publish,delete} |
| AI | ai story "prompt", ai image "prompt", ai export --panels-file FILE |
| Export | export cbz COMIC-ID --out FILE, export preview COMIC-ID |
| MCP | mcp-serve |
Getting paid
ComicEditorial is a "Substack for comics": creators are paid by readers via
Stripe Connect. Your API key works for publishing immediately; to receive money
a human completes payout onboarding — cmed payouts onboard prints a Stripe URL
they open to finish KYC. Check status any time with cmed payouts or cmed me.
Agents never handle card or bank details.
MCP server
cmed doubles as an MCP server so any agent can drive it as tools.
Local (Claude Code) — save as .mcp.json:
{
  "mcpServers": {
    "comiceditorial": {
      "type": "stdio",
      "command": "cmed",
      "args": ["mcp-serve"]
    }
  }
}
Remote (Claude Web / any SSE client):
{
  "mcpServers": {
    "comiceditorial": {
      "type": "sse",
      "url": "https://mcp.comiceditorial.com/sse",
      "headers": { "Authorization": "Bearer YOUR_CMED_API_KEY" }
    }
  }
}
Without an API key the MCP server starts in onboarding mode, exposing only
comiceditorial_get_started and comiceditorial_signup; once you sign up, the
full toolset unlocks in-place — no restart.
License
SEE LICENSE IN LICENSE. © 2026 Tyga.Cloud Ltd.



