RepoPilot


Deterministic review for code you didn't write.
Coding agents and busy teams produce more diffs than anyone can carefully
read. RepoPilot is a local Rust CLI that inspects a Git change and reports,
with structural evidence, where it crosses security boundaries, changes
behavior, and how far it reaches through the import graph. There is no LLM
inside and nothing leaves your machine: the same diff always produces the
same answer, so you can gate CI on it.
Sixty seconds: an agent "optimizes" image uploads
An agent is asked to shell out to mogrify after image edits in a Django
app (Wagtail). The diff is one file, +12 −6, and it works. It also quietly
drops a permission check and pipes request input into a shell.
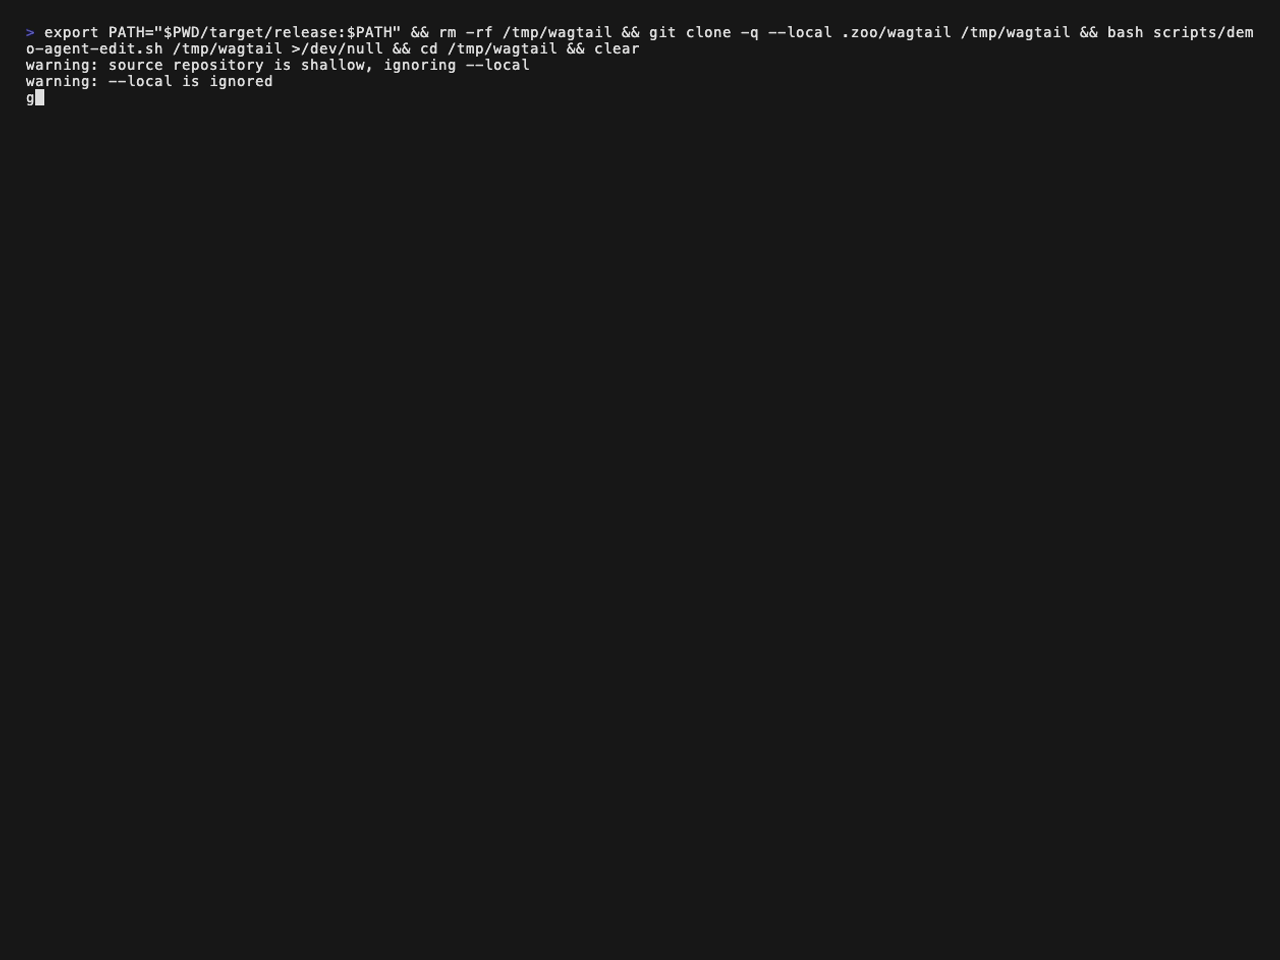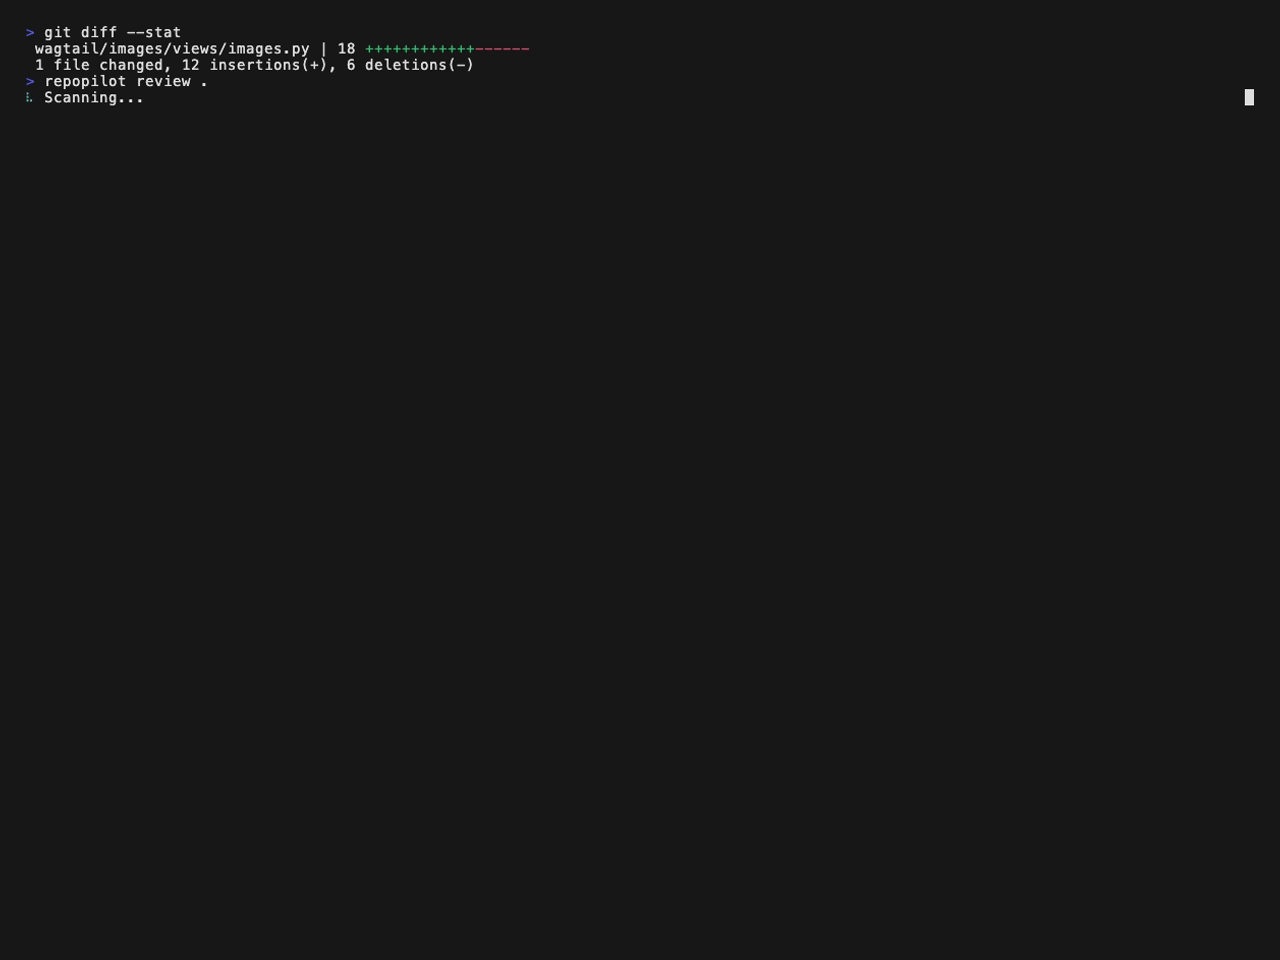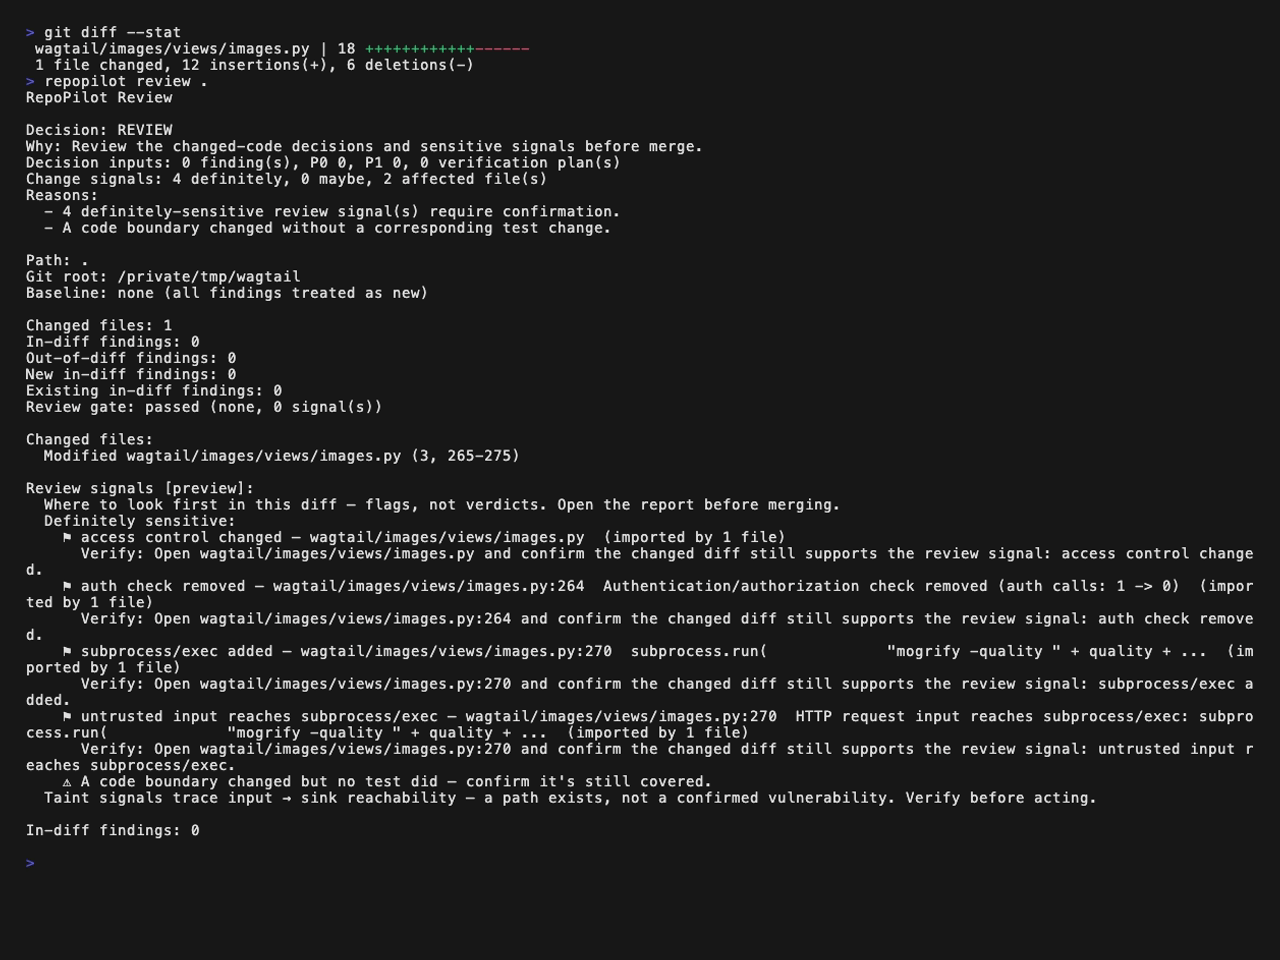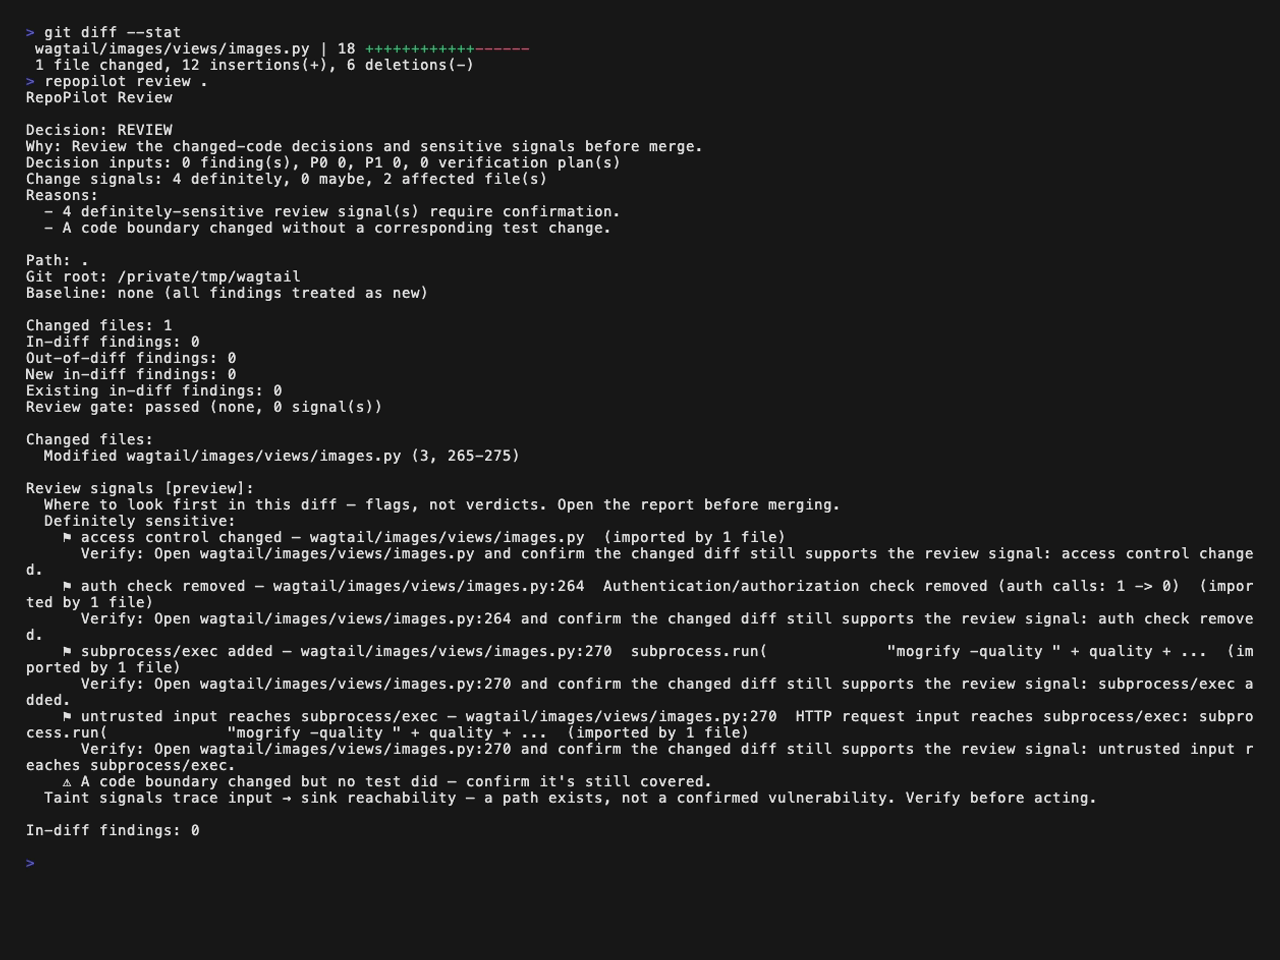
One command, repopilot review ., and the diff answers for itself — one
verdict, the reasons behind it, and one next action, then the evidence:
Decision: REVIEW (Change Proof: REVIEW)
Reasons:
  - Definitely-sensitive review signal(s) require confirmation.
  - A changed boundary has no corresponding test change.
  …
Next action: Resolve or confirm the high-priority findings and sensitive signals listed below before merge.

⚑ access control changed — wagtail/images/views/images.py
⚑ auth check removed — wagtail/images/views/images.py:264
    Authentication/authorization check removed (auth calls: 1 -> 0)
⚑ subprocess/exec added — wagtail/images/views/images.py:270
⚑ untrusted input reaches subprocess/exec — wagtail/images/views/images.py:270
    HTTP request input reaches subprocess/exec: subprocess.run("mogrify -quality " + quality + ...
⚠ A code boundary changed but no test did — confirm it's still covered.
The edit is scripted so you can replay it on the pinned Wagtail checkout
RepoPilot uses for regression testing — but it is the kind of diff agents
ship every day:
python3 scripts/zoo.py clone --only wagtail
scripts/demo-agent-edit.sh .zoo/wagtail
repopilot review .zoo/wagtail
The same review works across languages — the identical flow in a Spring
controller (scripts/demo-java-agent-edit.sh on the pinned PetClinic
checkout) is caught the same way.
RepoPilot reports structural evidence, not a security verdict. A flagged
flow is a path to verify, not a confirmed vulnerability. Use it beside
tests, linters, and dedicated security tools.
VERIFIED is only awarded when checks you configure and select with
--verify pass on the reviewed revision; repopilot init --suggestions-output repopilot-suggestions.toml proposes them for your stack without applying
anything. Add --detail full for provenance, legacy readiness, and ownership.
Catch broken code, not just risky code
A tidy-looking rename and file move — nothing a diff review would flag on its
own — quietly breaks two callers that still expect the old names. No compiler
runs; both are AST-plus-resolver proofs.
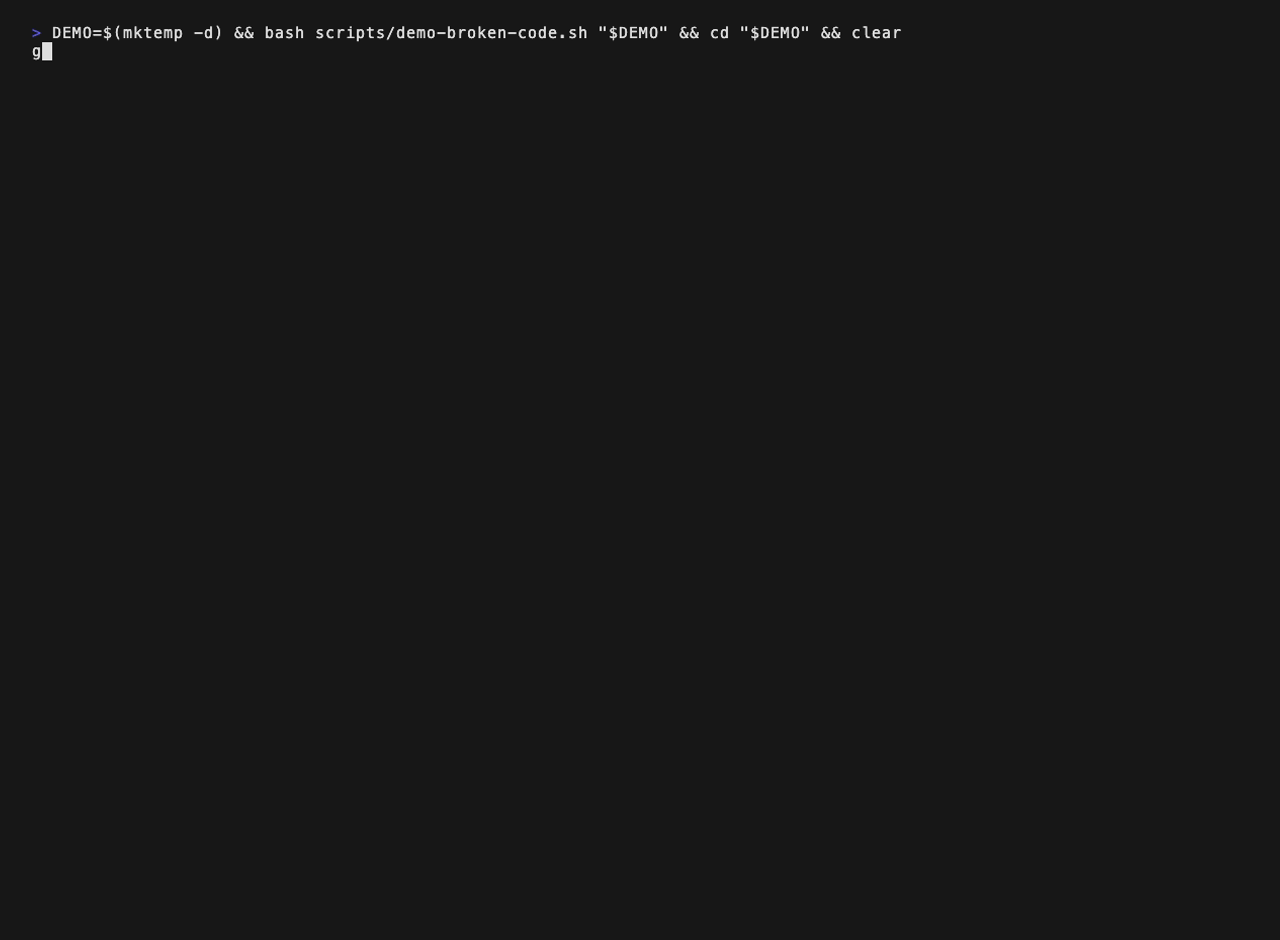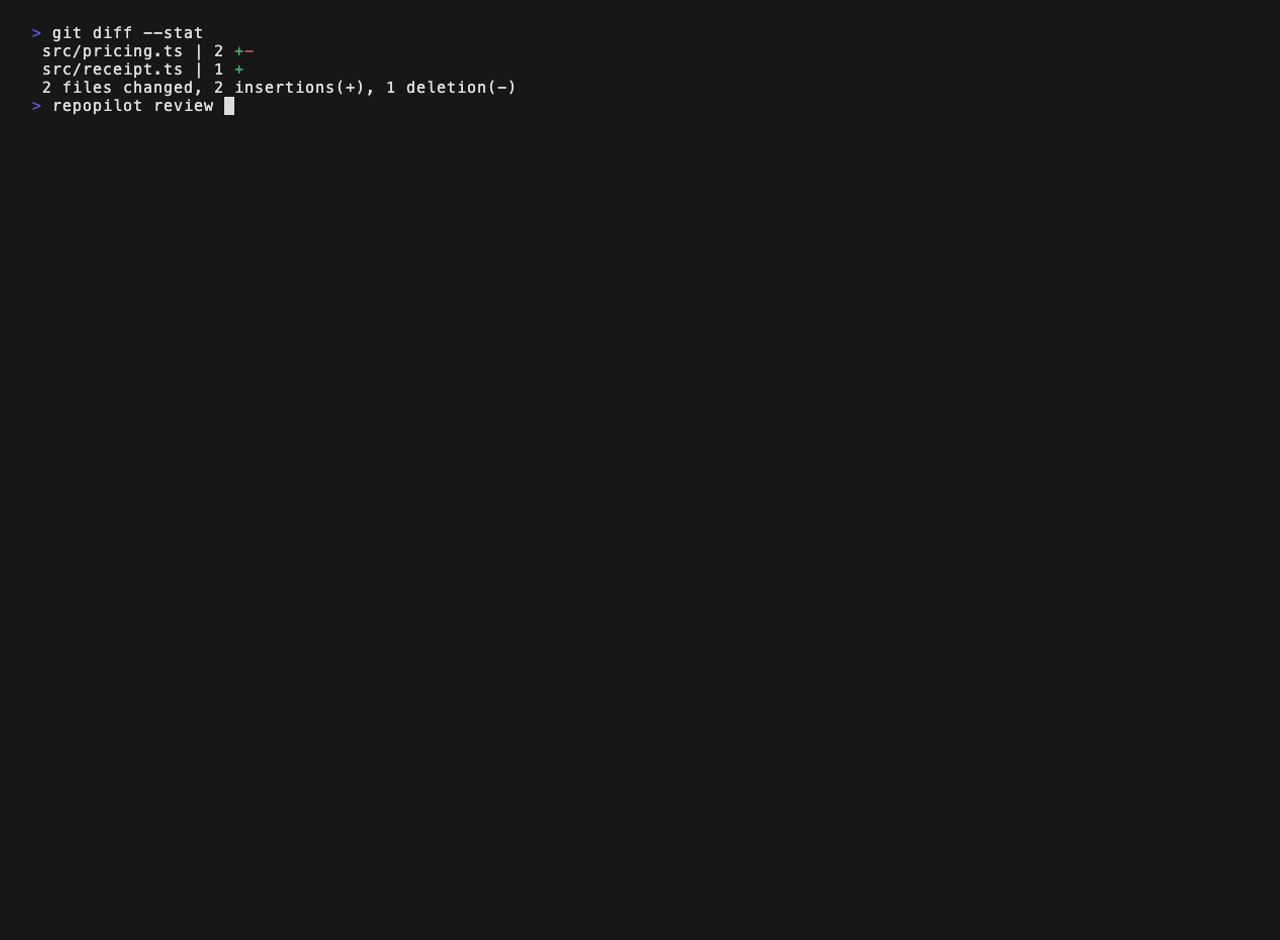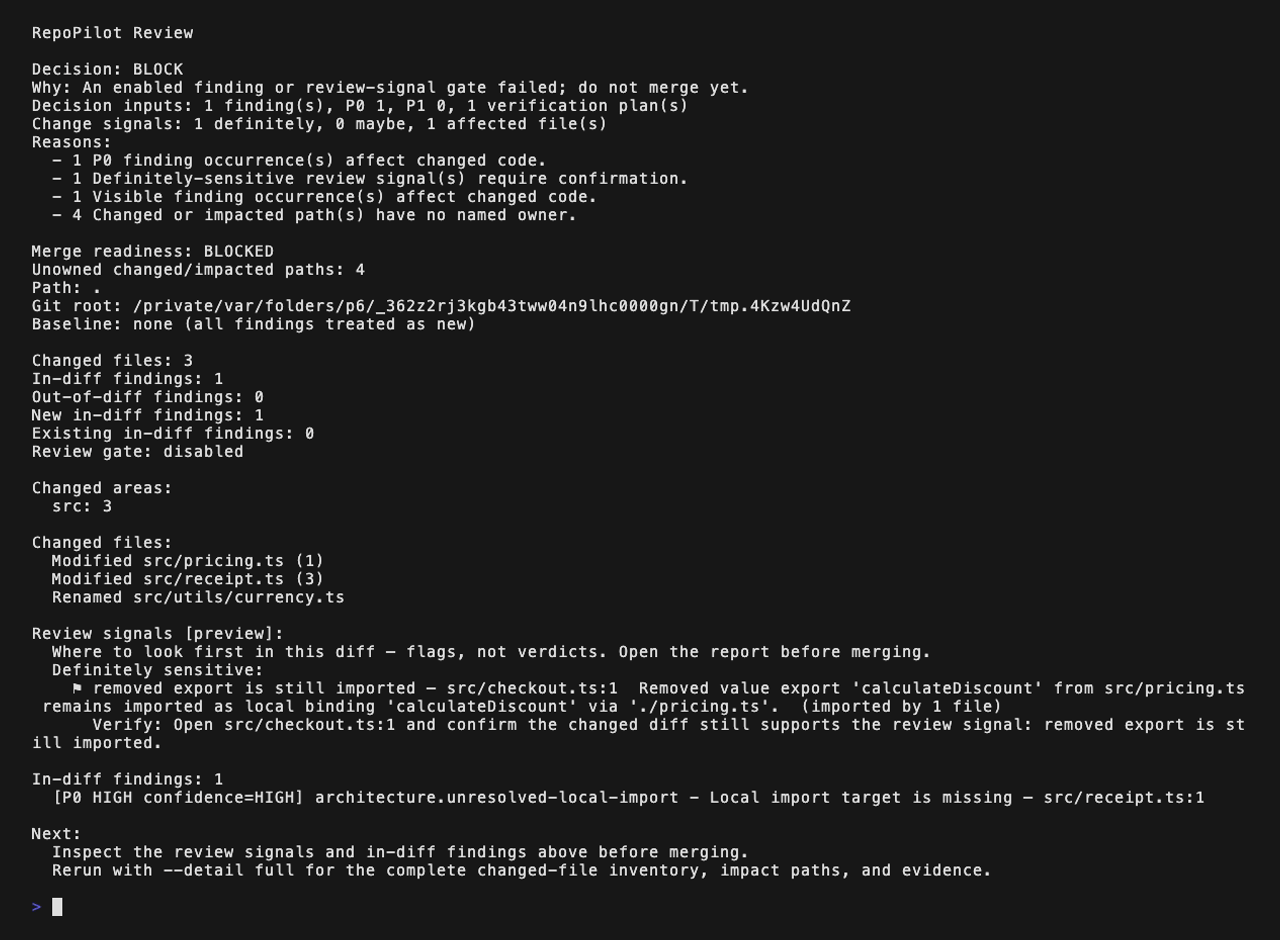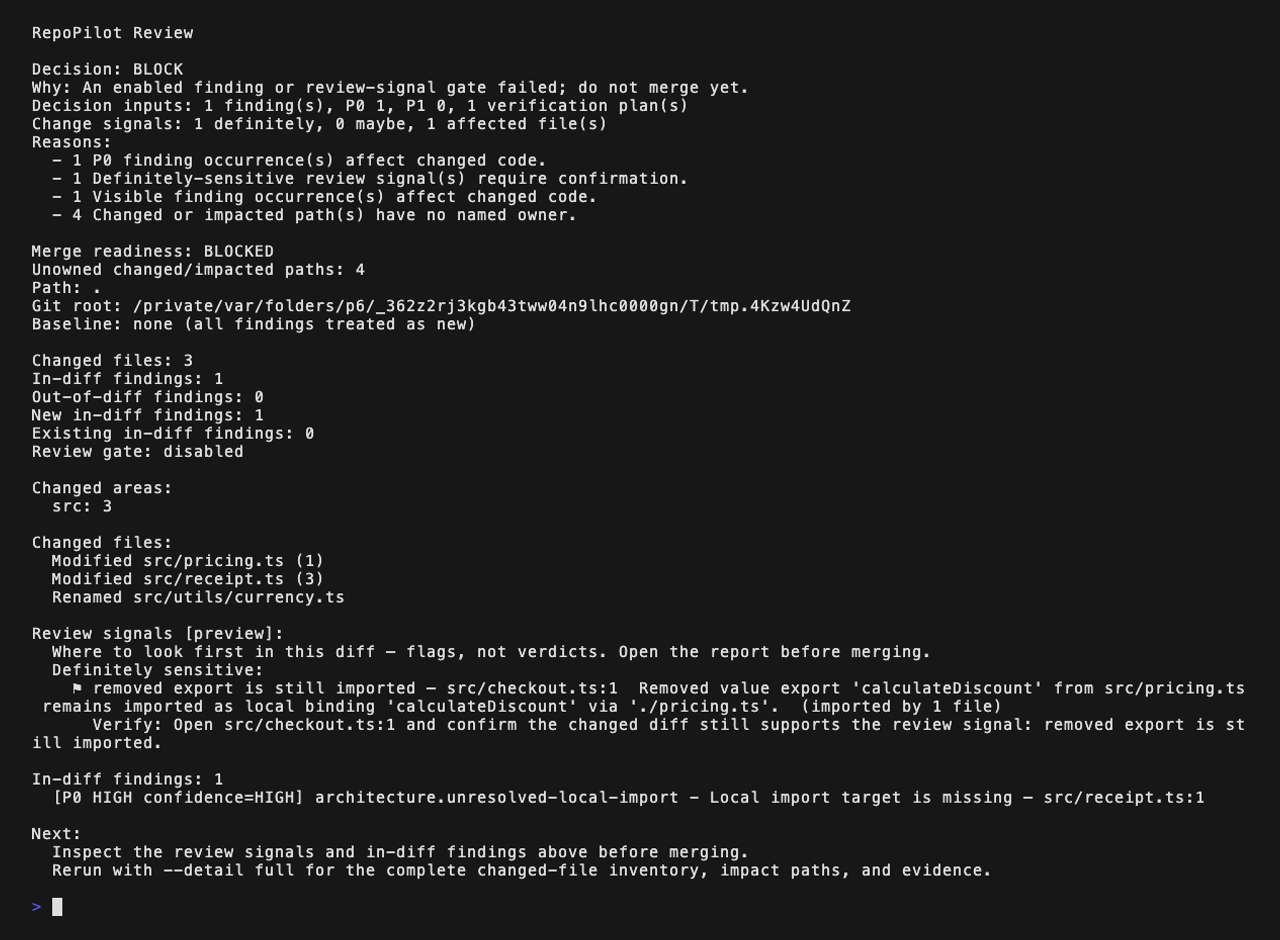
scripts/demo-broken-code-review.sh
Why not an LLM reviewer?
- Deterministic. Same diff in, same signals out. You can gate a pipeline
on it and reproduce any result; there is no prompt to drift and no model
to update under you.
- Local. No source upload, no API key, no per-review cost, no telemetry.
It runs offline, including the MCP server.
- Evidence, not opinions. Every signal points at a line and states the
structural fact behind it — an auth call count that went down, a request
value reaching
subprocess.run. Nothing "looks fine."
LLM reviewers are useful; a deterministic layer under them is what makes
their output checkable.
Install
cargo install repopilot
npm install -g repopilot
Homebrew, GitHub Releases, and source builds:
Installation.
Review a change
repopilot review .
repopilot review . --base origin/main
Review groups evidence into tiers: security boundaries (access control,
request trust, deploy surface, supply chain, secrets), behavioral changes
(network, subprocess, filesystem, SQL, removed error handling or auth),
algorithmic shifts, taint-lite flows (changed request/process input reaching
SQL, exec, filesystem-write, or network sinks), broken local imports and
exports (a deleted or renamed file still imported, a removed export still
called under its old name — no compiler required), and blast radius (files
that import what changed).
Signals are advisory by default. Gate CI on the high-confidence tier:
repopilot review . --base origin/main --fail-on-review definitely
Every review also resolves to one merge-readiness verdict — ready,
review, or blocked — built from findings, review signals, CODEOWNERS,
and blast radius, with deterministic reason codes and suggested owners.
Console, Markdown, JSON, MCP, and the GitHub Action summary all read the same
ChangeProof and evidence records; machine projections keep the legacy fields
for compatibility.
Compare risk across runs
History is local, bounded, and off by default. Record two compatible
analyses to see what's new, persisting, resolved, or changed severity —
nothing leaves your machine:
repopilot review . --record-history
repopilot scan . --record-history
Receipts live under .repopilot/history/.
To calibrate a known rule to your repository instead of silencing it
project-wide, add a scoped, diffable entry to .repopilot/overlay.toml:
[[overlay]]
rule = "behavioral.panic-risk"
path = "src/cli/**"
severity = "low"
reason = "CLI handlers can terminate on unrecoverable input"
Overlay decisions stay visible in --profile strict and the decision
trace — never a silent post-scan filter. Details:
Configuration.
Guard an agent run
Take a snapshot before the agent starts, review everything it did — commits
and uncommitted edits — when it stops:
repopilot snapshot
repopilot review --since-snapshot
To wire this in permanently — a Claude Code hook that reviews every agent
session, an MCP server the agent can query mid-task (repopilot init --mcp-client claude|cursor|generic), or a PR gate via the GitHub Action —
see Guard your agent runs.
Beyond the diff
repopilot scan . — full-repository audit (architecture, coupling,
framework, testing). repopilot baseline create . adopts existing debt so
only new findings gate.repopilot ai context . — one compact Markdown handoff of repository
facts, findings, and a prioritized fix plan for an external assistant.
Local, no LLM calls.repopilot mcp --root . — the same analysis over stdio for coding agents:
synchronous, root-confined, offline.
Details: Common workflows.
Documentation
Contributing and development commands: CONTRIBUTING.md.
License
MIT OR Apache-2.0.



