

Security News
Happy Birthday, Shai-Hulud
It has been one year since Shai-Hulud made its first appearance on npm.
By Sarah Gooding - Sep 18, 2026
rustpad-mcp
Advanced tools




A Model Context Protocol server for Rustpad, the efficient, minimal, self-hosted collaborative text editor.
It gives an AI assistant read and write access to the pads of a Rustpad
instance. Reads go through Rustpad's HTTP API; writes speak the
operational-transformation WebSocket protocol, so targeted edits
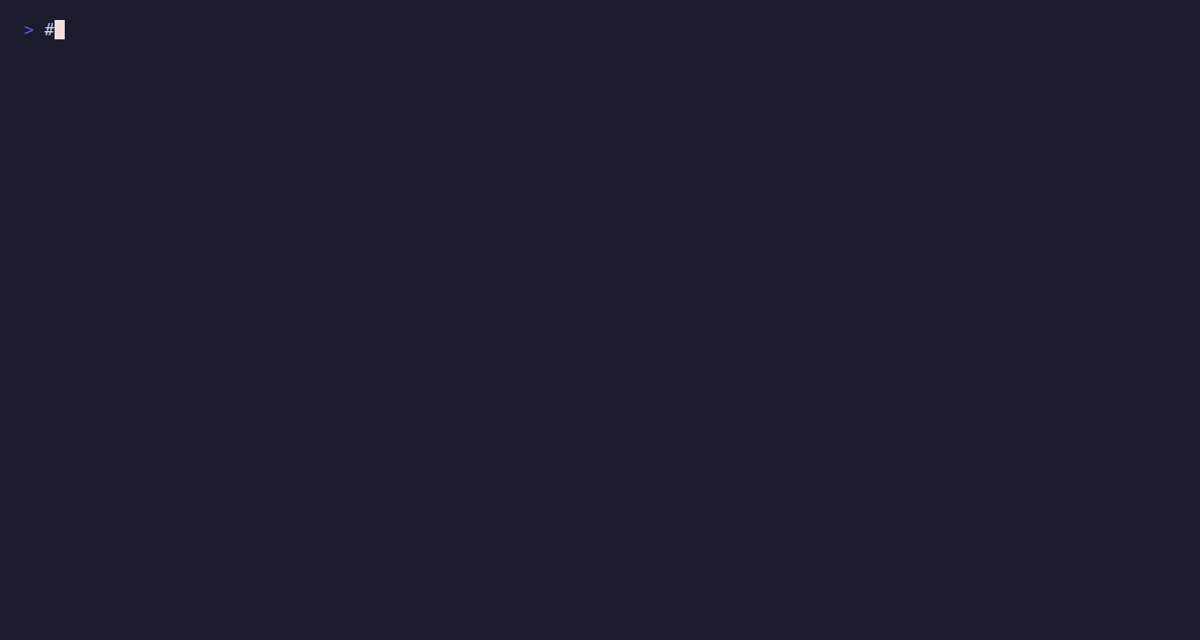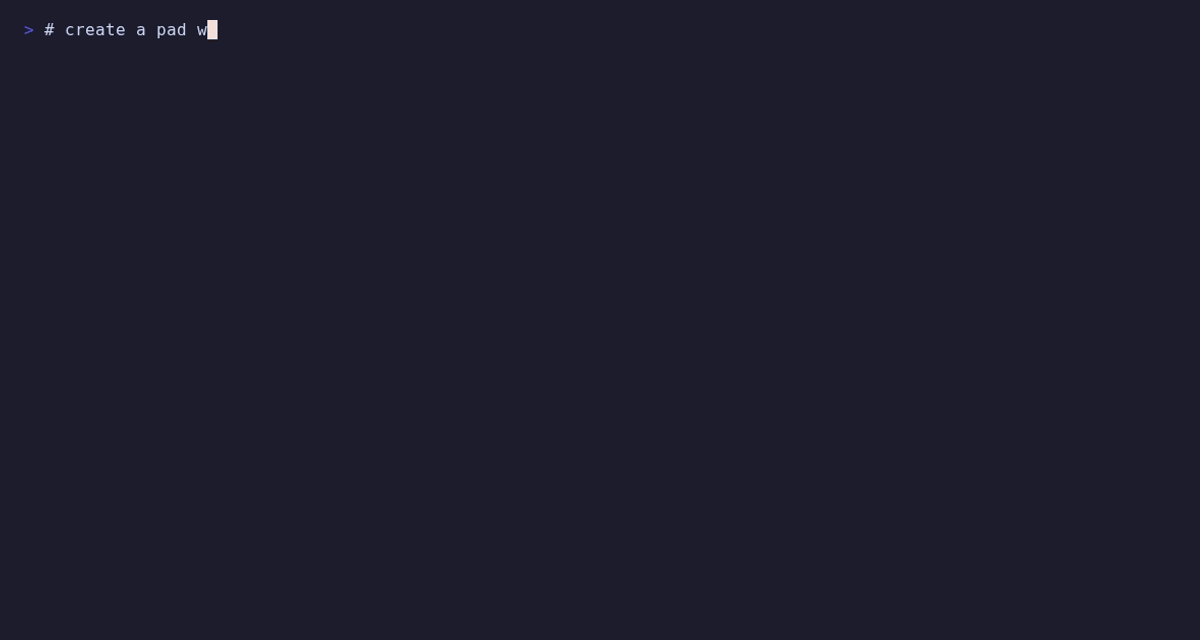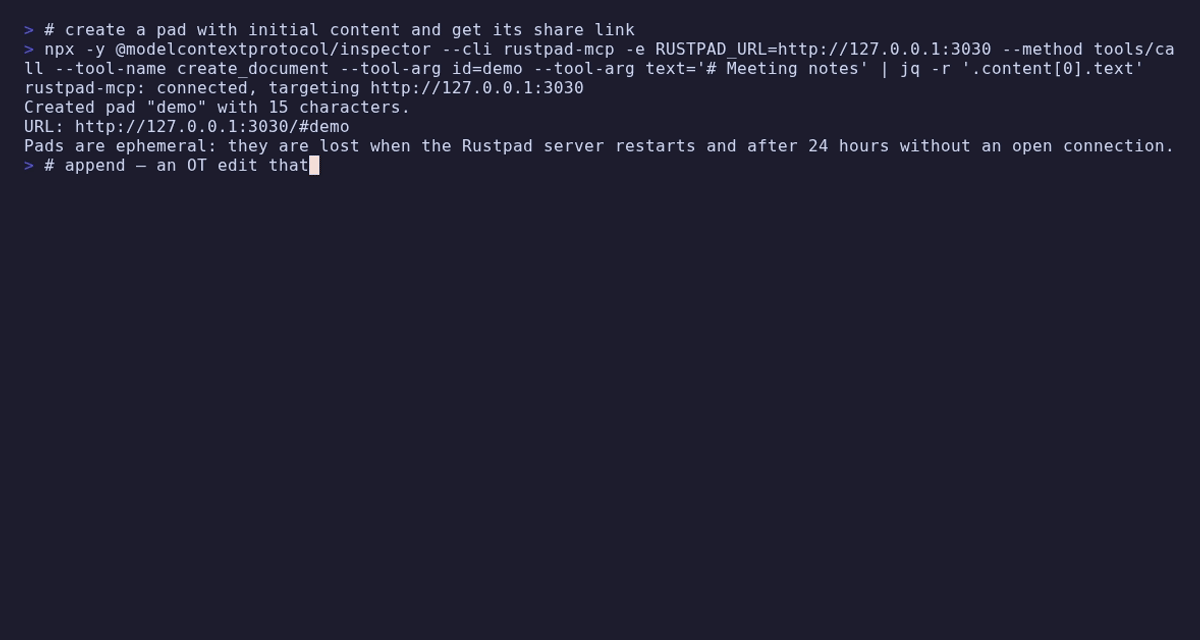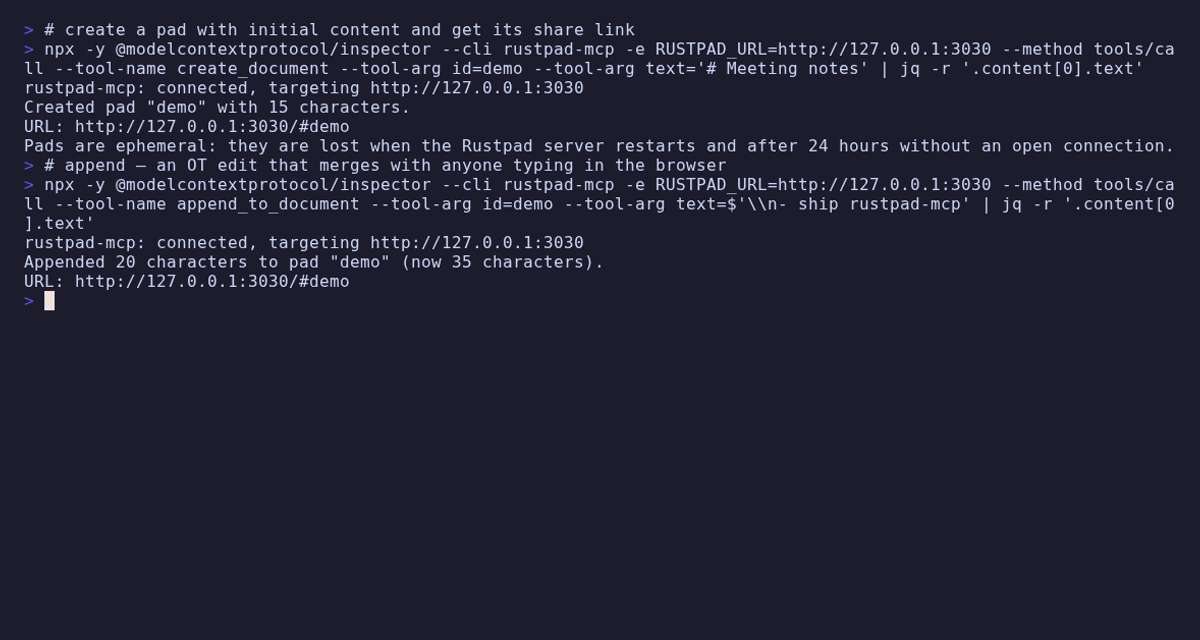
(append_to_document, replace_in_document) merge cleanly with what human
collaborators type at the same time instead of overwriting it. While the
server edits a pad, it is visible to everyone in the pad as a collaborator
named rustpad-mcp.
📖 Full documentation at rustpad-mcp.ni-c.de

| Variable | Required | Description |
|---|---|---|
RUSTPAD_URL | yes | Base URL of the instance, e.g. https://rustpad.example.net |
RUSTPAD_READ_ONLY | no | true registers only the read tools |
RUSTPAD_INSECURE_TLS | no | true accepts self-signed certificates (scoped to this connection only) |
The same URL serves the HTTP API, the WebSocket endpoint and the share links
returned by the tools (<RUSTPAD_URL>/#<pad-id>). Booleans must be exactly
true. The server starts and lists its tools without configuration; every
call then fails with setup instructions.
Keep in mind what Rustpad is: pads are ephemeral (lost on server restart
and after 24 hours of inactivity, unless the instance is run with
SQLITE_URI) and anyone who knows a pad id can read and write it. Do not
put secrets in pads.
claude mcp add rustpad --env RUSTPAD_URL=https://rustpad.example.net -- npx rustpad-mcp
{
  "mcpServers": {
    "rustpad": {
      "command": "npx",
      "args": ["rustpad-mcp"],
      "env": {
        "RUSTPAD_URL": "https://rustpad.example.net"
      }
    }
  }
}
~/.codex/config.toml:
[mcp_servers.rustpad]
command = "npx"
args = ["-y", "rustpad-mcp"]

[mcp_servers.rustpad.env]
RUSTPAD_URL = "https://rustpad.example.net"
docker run -i --rm -e RUSTPAD_URL=https://rustpad.example.net ghcr.io/ni-c/rustpad-mcp
| Tool | Description |
|---|---|
get_document | Read the plain-text content of a pad |
get_document_info | Content length, revision, language and the users editing right now |
get_stats | Server statistics (uptime, number of documents) |
create_document | Create a pad (random or chosen id), optionally with content and language |
set_document | Replace the entire content — non-empty pads require a confirmation token |
append_to_document | Append text; concurrent edits elsewhere survive |
replace_in_document | Exact search & replace via OT; unique match required unless replace_all |
set_language | Set the Monaco syntax-highlighting language |
With RUSTPAD_READ_ONLY=true only the first three are registered.
RUSTPAD_INSECURE_TLS relaxes certificate validation only for the
configured connection, never process-wide.npm install
npm run lint && npm run build && npm test
The test suite talks to an in-memory fake of rustpad-server (including OT
transformation of concurrent edits) over the real MCP protocol; no live
instance is needed. The architecture diagram and social card are generated —
edit docs/assets/architecture.source.svg and run npm run assets, never the
rendered copies.
Releases are tag-driven. Bump package.json, move the [Unreleased] notes in
CHANGELOG.md under the new version, commit, then:
git tag -s vX.Y.Z -m "vX.Y.Z"
git push origin main vX.Y.Z
The release workflow publishes to npm via Trusted Publishing (OIDC, with provenance), pushes the multi-arch container image to GHCR, creates the GitHub release from the CHANGELOG section, and updates the entry in the official MCP registry.
MIT © Willi Thiel
FAQs
MCP server for Rustpad, the self-hosted collaborative text editor
The npm package rustpad-mcp receives a total of 41 weekly downloads. As such, rustpad-mcp popularity was classified as not popular.
We found that rustpad-mcp demonstrated a healthy version release cadence and project activity because the last version was released less than a year ago. It has 1 open source maintainer collaborating on the project.
Security News
It has been one year since Shai-Hulud made its first appearance on npm.

Research
/Security News
Operators behind PolinRider used a compromised GitHub account to plant malware in four development versions of a Packagist package with 700,000+ downloads.

Security News
GitHub Actions now supports cache-mode, a least-privilege control on the Actions cache aimed at the cache poisoning technique behind recent compromises.