
Security News
Re-Enabled GitHub Actions Expose Thousands of Repositories to Mini Shai-Hulud
Two compromised GitHub Actions were re-enabled with malicious tags intact, exposing thousands of downstream repositories to Mini Shai-Hulud.
apollo-server-next
Advanced tools
This project was bootstrapped with [TSDX](https://github.com/jaredpalmer/tsdx).
This project was bootstrapped with TSDX.
Below is a list of commands you will probably find useful.
npm start or yarn startRuns the project in development/watch mode. Your project will be rebuilt upon changes. TSDX has a special logger for you convenience. Error messages are pretty printed and formatted for compatibility VS Code's Problems tab.
Your library will be rebuilt if you make edits.
npm run build or yarn buildBundles the package to the dist folder.
The package is optimized and bundled with Rollup into multiple formats (CommonJS, UMD, and ES Module).
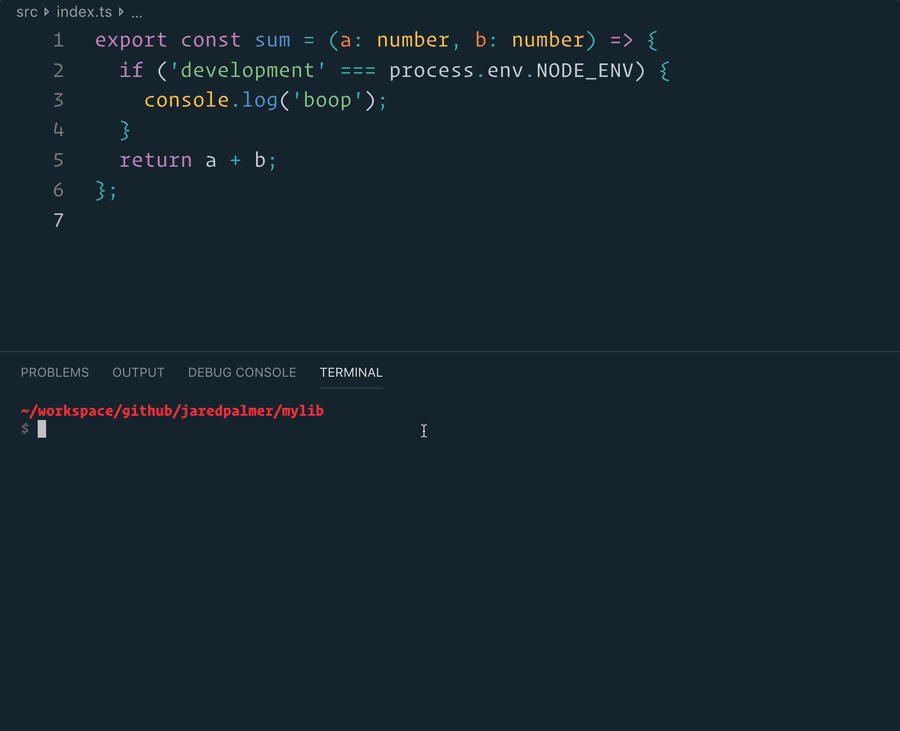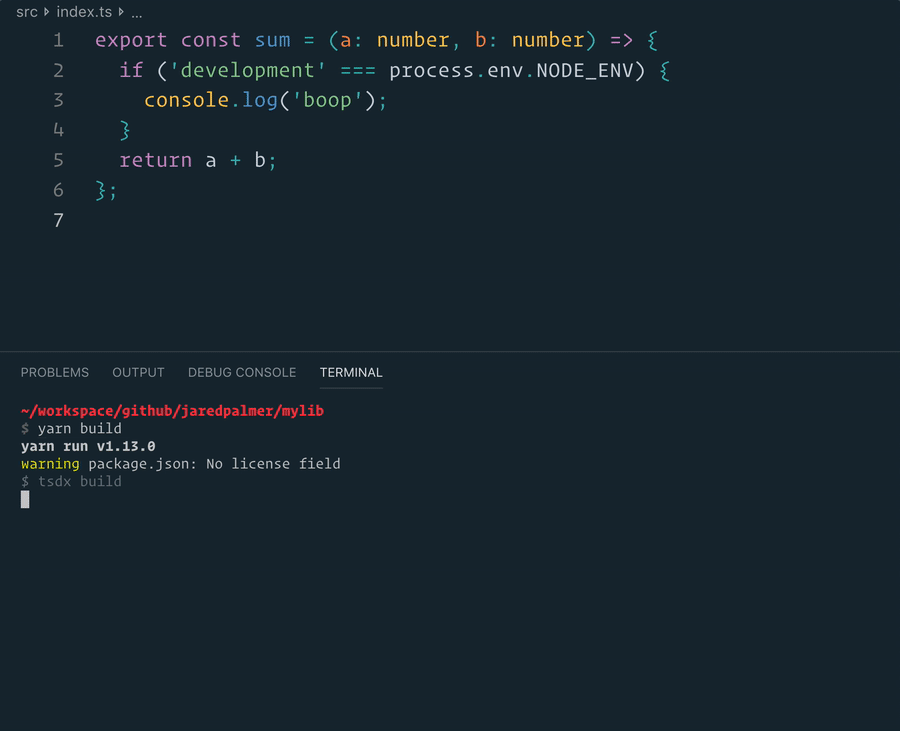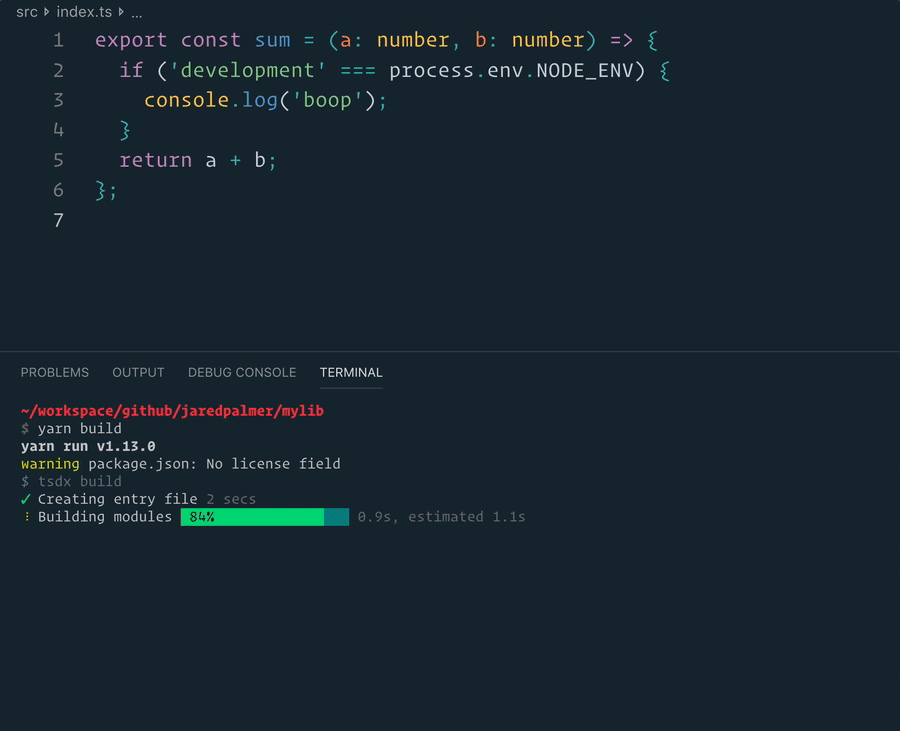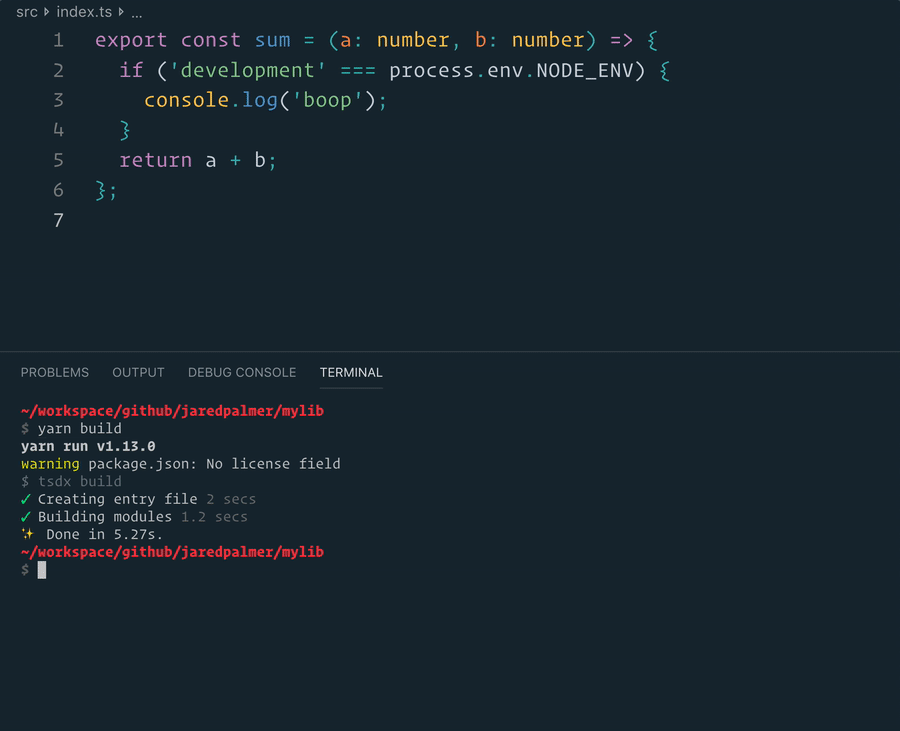
npm test or yarn testRuns the test watcher (Jest) in an interactive mode. By default, runs tests related to files changed since the last commit.
FAQs
This project was bootstrapped with [TSDX](https://github.com/jaredpalmer/tsdx).
The npm package apollo-server-next receives a total of 0 weekly downloads. As such, apollo-server-next popularity was classified as not popular.
We found that apollo-server-next demonstrated a not healthy version release cadence and project activity because the last version was released a year ago. It has 1 open source maintainer collaborating on the project.

Security News
Two compromised GitHub Actions were re-enabled with malicious tags intact, exposing thousands of downstream repositories to Mini Shai-Hulud.

Research
/Security News
A malicious Firefox extension fetches its payload after installation to evade detection, steal Google session cookies, and automate account takeover.

Research
/Security News
The compromise affects MemTensor's MemOS, an open source memory framework for large language models (LLMs) and AI agents. Both npm package @memtensor/memos-cloud-openclaw-plugin and the PyPI package MemoryOS are compromised. They drop cross-platform Go binaries that exfiltrate developer secrets.


